IPsec site-to-site VPN with Sophos XG
1. Log in to the Vipilink portal and create a network
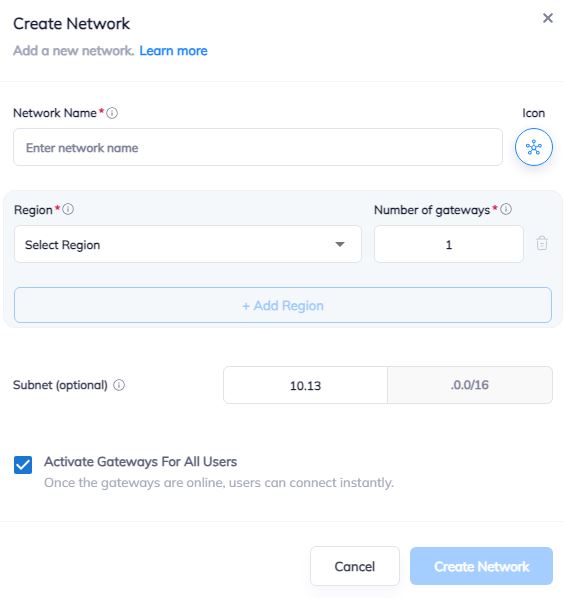
1.1 Go to Networks section and create a new network.
1.2 Define the network name.
1.3 Select the region and gateways number.
1.4 Choose the subnet.
1.5 Activate gateways for all users section is active by default. If you want to disable this function - just remove the mark.
2. Create the IPsec tunnel in the Vipilink portal
2.1 Go to Networks section and click on the subnet that you created in Step-1.
2.2 Click on Gateway and add a Tunnel. Choose IPSec Site-to-Site Tunnel and press to continue.
2.3 Choose between a Single-Tunnel and Dual-Tunnel.
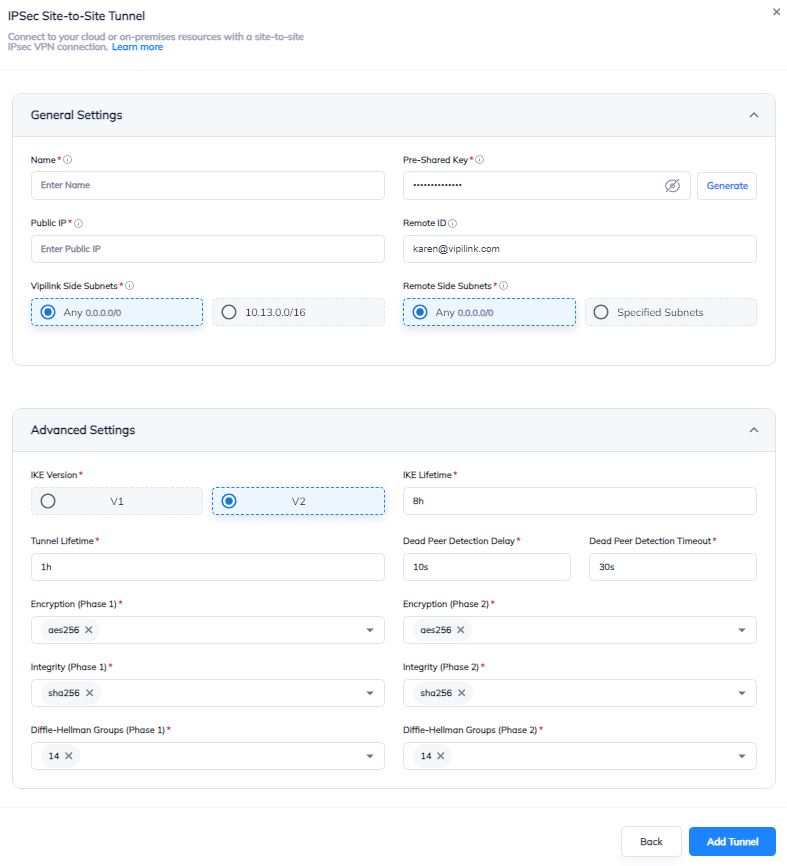
2.4 General Settings Values
-
Name
-
Public IP
-
Vipilink Side Subnets
-
Pre-Shared Key
-
Remote ID
-
Remote Side Subnets
2.5 Advanced Settings Values
-
Ike Version
-
Tunnel Lifetime
-
Encryption (Phase 1)
-
Integrity (Phase 1)
-
Diffie-Helman Groups (Phase 1)
-
Ike Lifetime
-
Dead Peer Detection Delay
-
Dead Peer Detection Timeout
-
Encryption (Phase 2)
-
Integrity (Phase 2)
-
Diffie-Helman Groups (Phase 2)
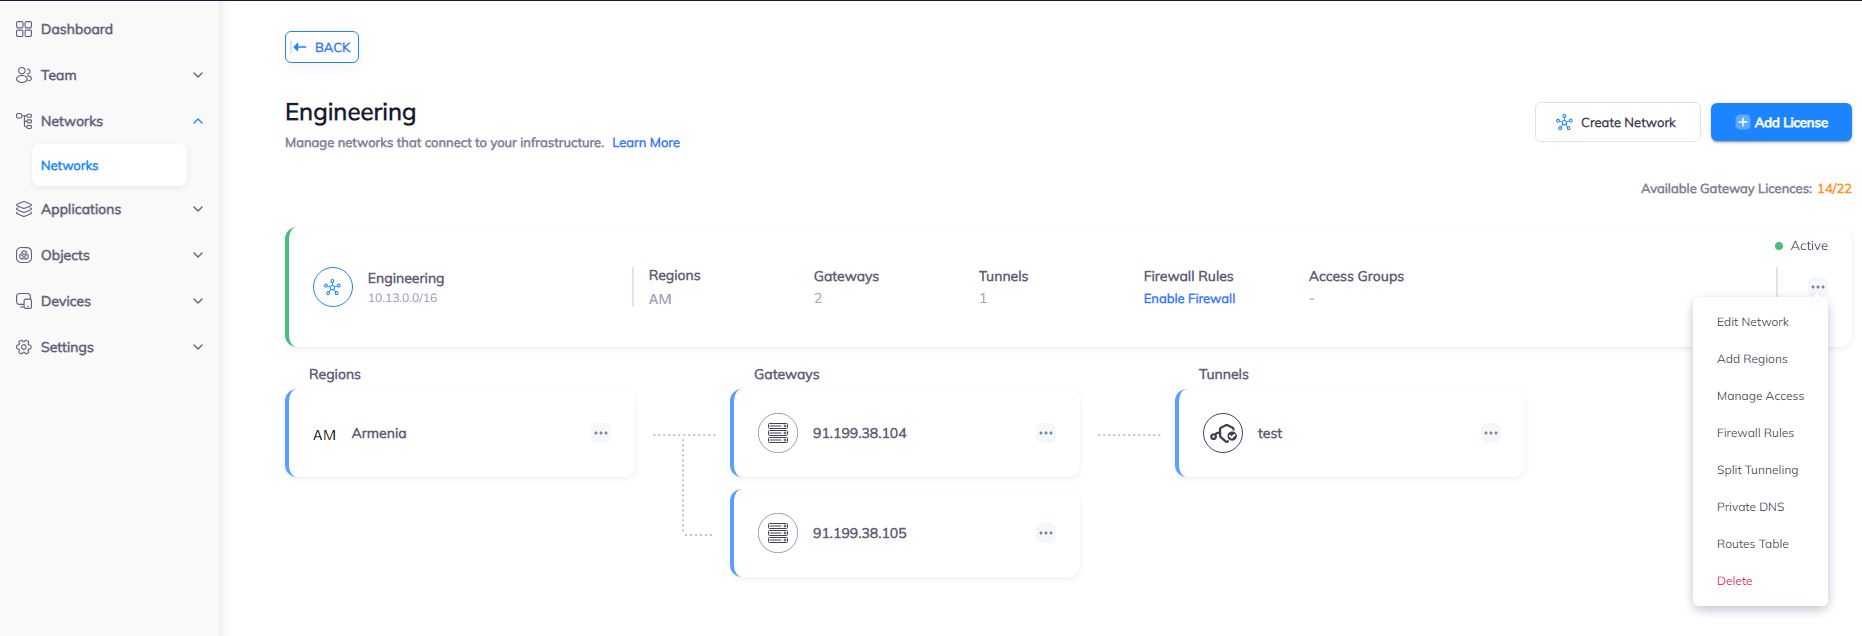
2.6 You can also manage a Network, Regions, Access, Firewall Rules, Route Table, enable Split Tunneling and Private DNS.
3. Create the IPsec tunnel on Sophos XG
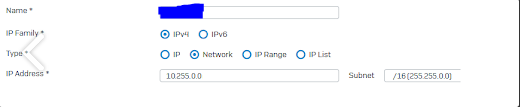
3.1 Log in to the Sophos XG Web Interface, navigate to Host and Services, and create a new object of local network.
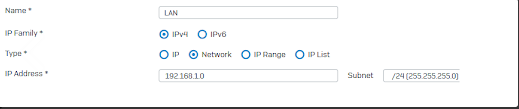
3.2 Create a new object of Vipilink network.
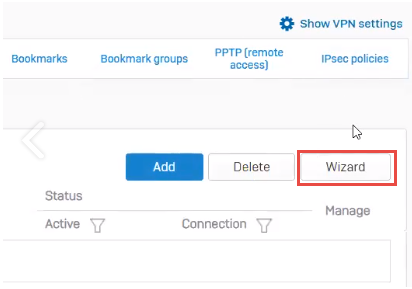
3.3 Go to VPN/Connections and select Wizard to create a new connection.
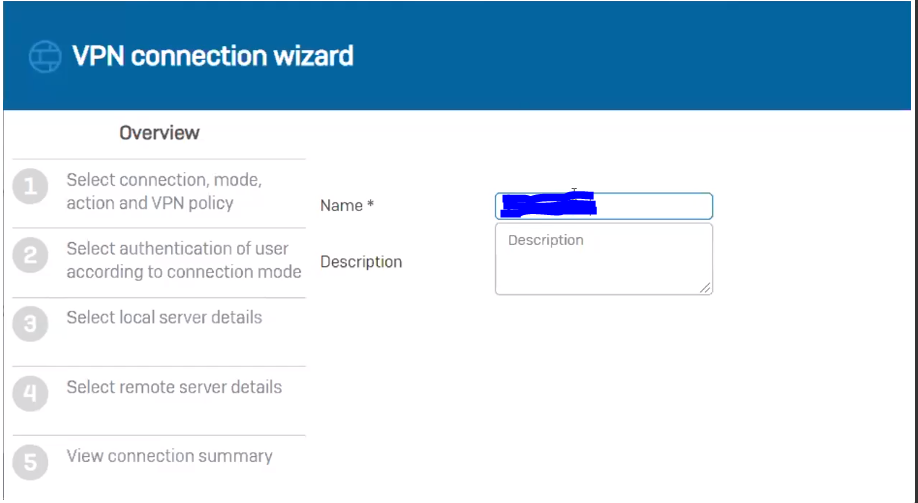
3.4 Define the name and description for the connection.
3.5 Click Start to proceed.
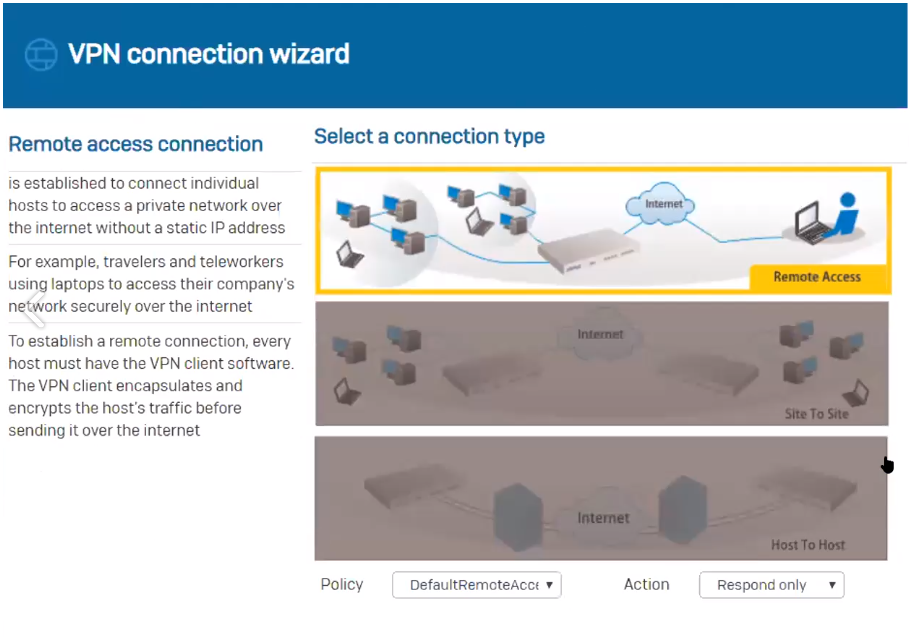
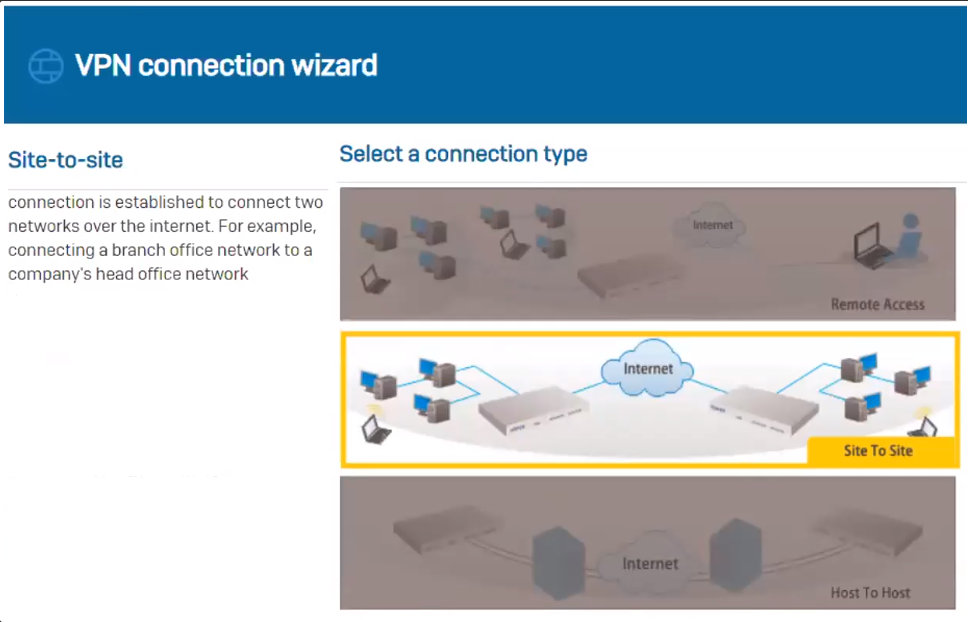
3.6 Choose Site-to-site as the connection type and select Head Office.
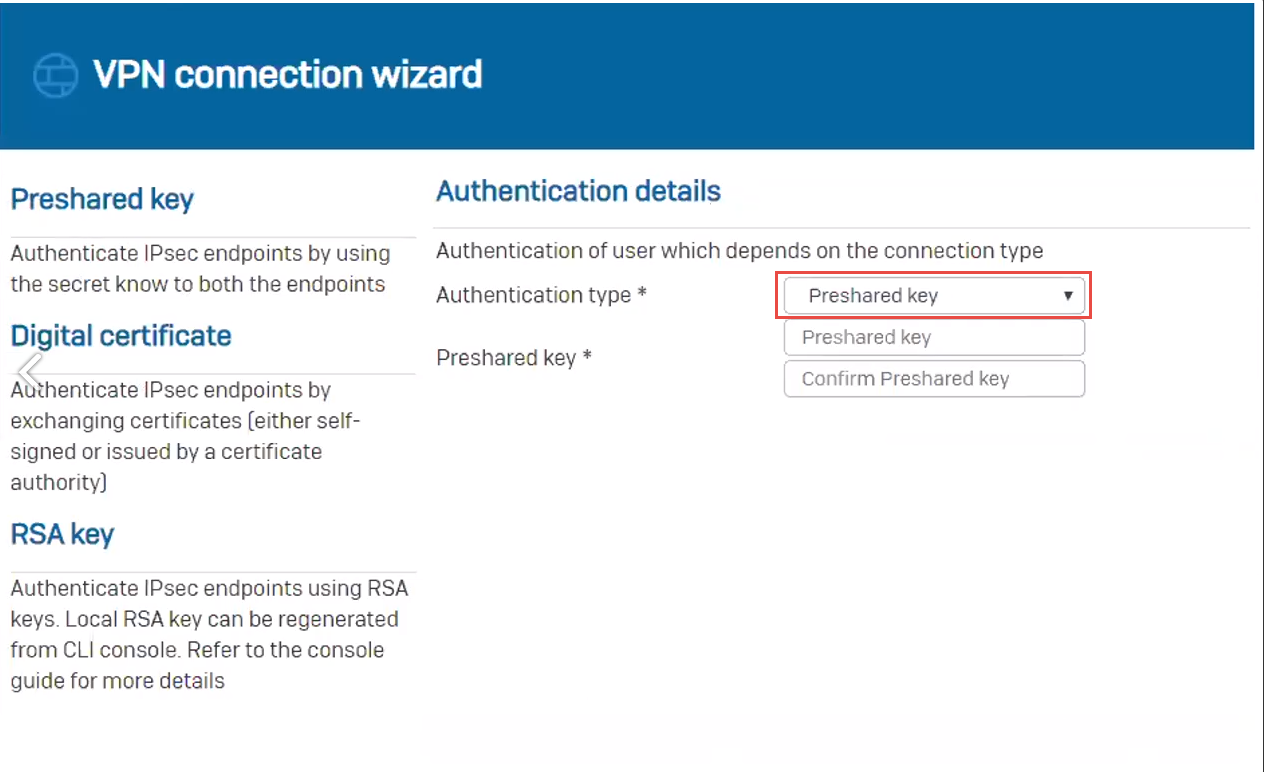
3.7 Select Authentication Type to preshared key.
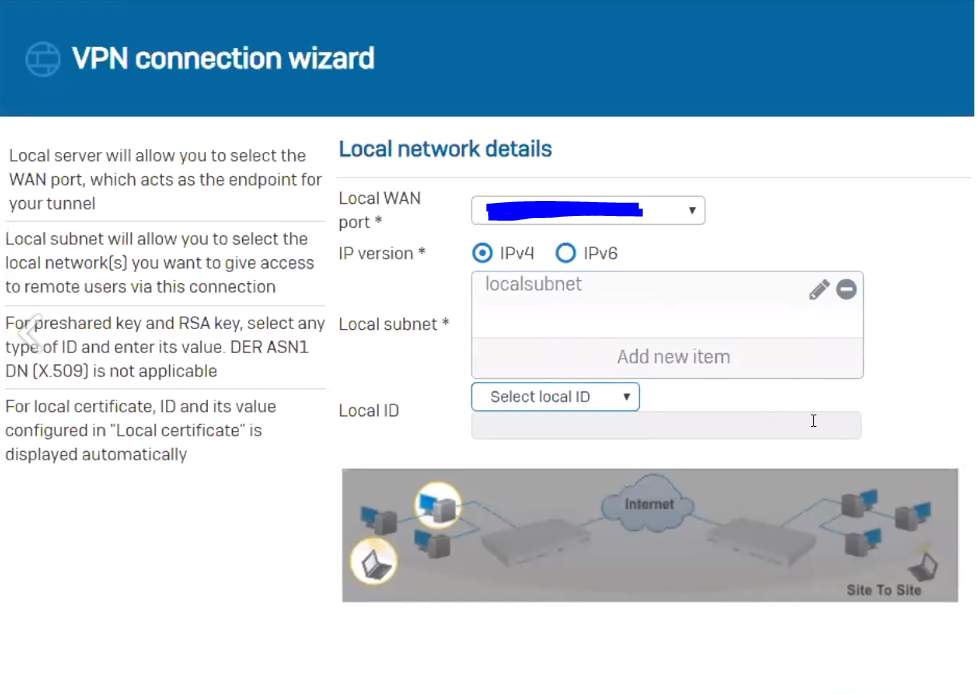
3.8 Parameters of the Local network details section.
-
Local WAN port - WAN
-
IP version - IPv4
-
Local subnet - choose the object created in step 3.1
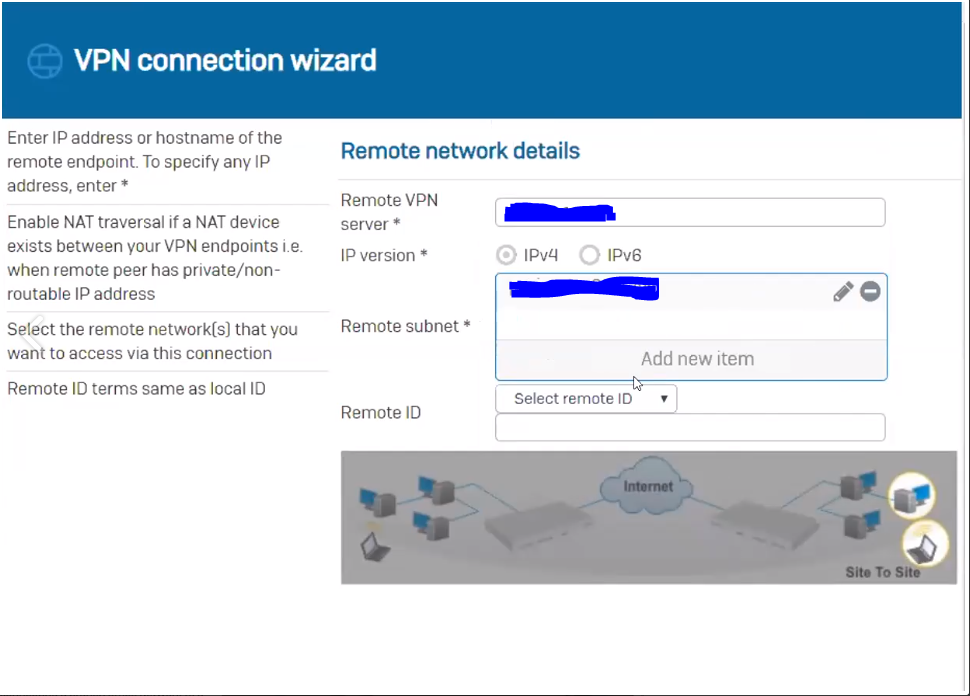
3.9 Parameters of the Remote network details section.
-
Remote VPN server - Vipilink IP Address
-
IP version - IPv4
-
Remote subnet - choose the object created in step 3.2
3.10 The User Authentication Mode must be disabled.
3.11 Click Finish. Connection status should be Active.
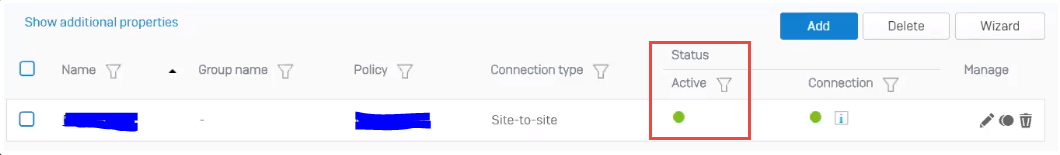
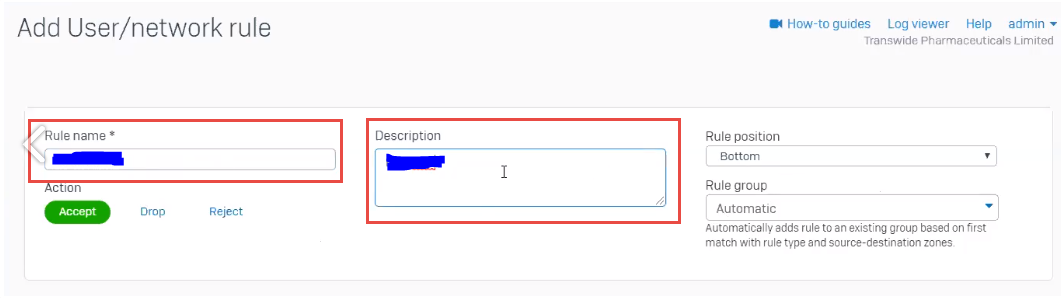
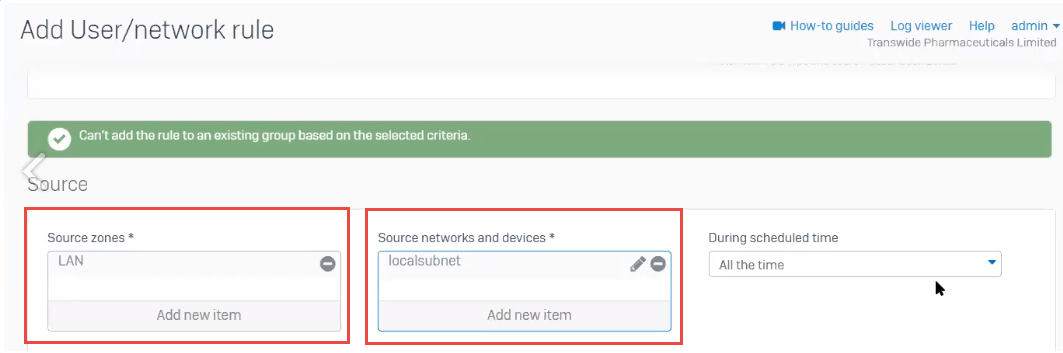
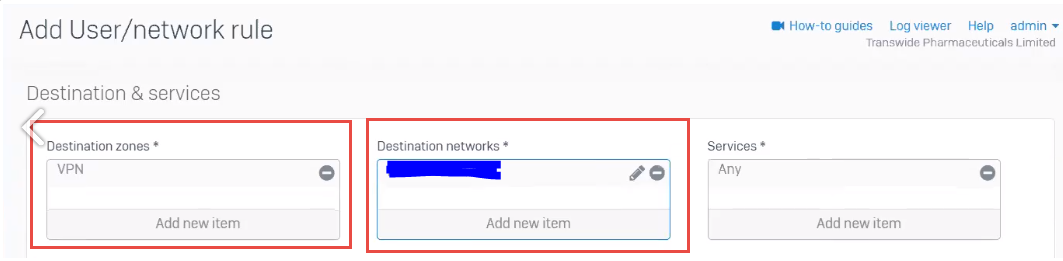
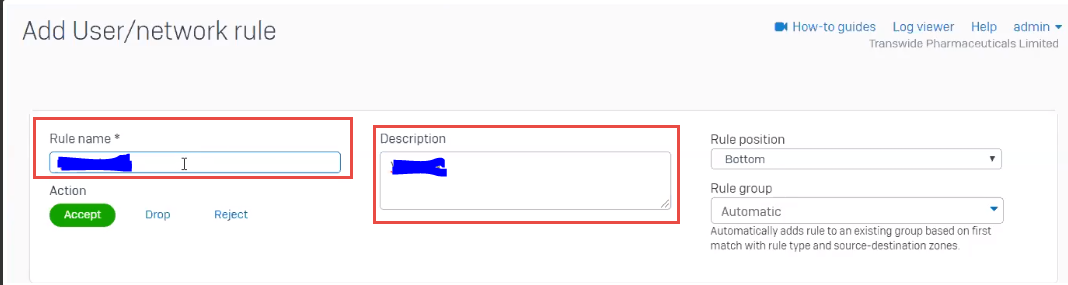
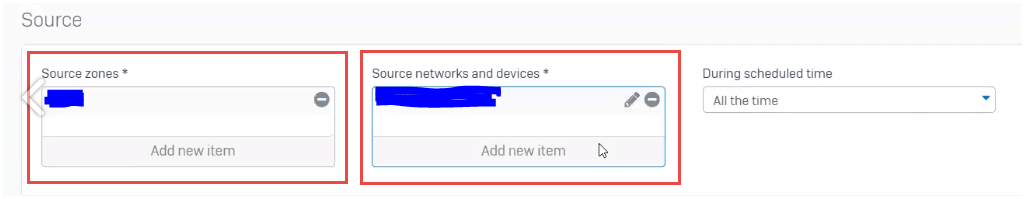
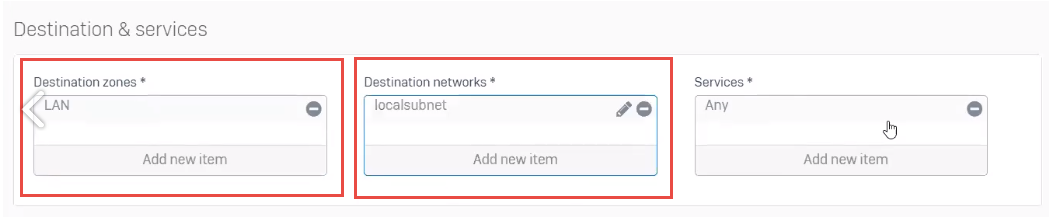
4.1 Navigate to Firewall and click Add Firewall Rule to allow VPN traffic to pass through. You need to add two User/network rules to allow traffic in both directions.
5.1 Verify connectivity between local and remote networks.
-
Use tools like ping or traceroute to check the connection
-
Ensure that resources on the remote network (e.g., shared folders, servers) are accessible from the local network.