AWS transit gateway
Connect a Vipilink network to one or more Amazon VPCs through an AWS transit gateway, with one IPsec tunnel between a Vipilink gateway and the transit gateway. Routing is static, and one Vipilink gateway is enough.
Use a transit gateway when you want to reach several VPCs through one tunnel, or when your VPCs are already connected to a transit gateway. If you only need one VPC, AWS virtual private gateway is simpler. If you need automatic failover, use AWS transit gateway with redundant tunnels.
Before you start
- A Vipilink network with at least one active gateway.
- An Amazon VPC, and permission to create transit gateway and VPN resources.
- The Vipilink network subnet and the VPC CIDR must not overlap.
- AWS charges by the hour for each transit gateway attachment and VPN connection, plus data processing.
How it fits together
| Where | What you create | What it does |
|---|---|---|
| AWS | Customer gateway | Tells AWS the public IP of your Vipilink gateway. |
| AWS | Transit gateway | The hub that connects your VPCs and the VPN. |
| AWS | VPC attachment | Connects your VPC to the transit gateway. |
| AWS | VPN attachment | Connects the transit gateway to Vipilink. Creating it also creates the Site-to-Site VPN connection. |
| AWS | Routes | One route in the transit gateway and one in the VPC send Vipilink traffic to the tunnel. |
| Vipilink | IPsec tunnel and route | The other end of the tunnel, and a route to the VPC. |
Example used on this page
| Item | Example value |
|---|---|
| Vipilink network | Remote Access, subnet 10.13.0.0/16 |
| Vipilink gateway | Frankfurt |
| AWS Region | US East (N. Virginia) |
| Amazon VPC | app-vpc, CIDR 10.50.0.0/16 |
| Customer gateway | vipilink-gw-frankfurt |
| Transit gateway | vipilink-tgw |
| VPC attachment | tgw-app-vpc |
| VPN attachment | vipilink-tgw-vpn-frankfurt |
| Site-to-Site VPN connection | vipilink-vpn-frankfurt |
| Vipilink tunnel | AWSTransit |
Replace these with your own values.
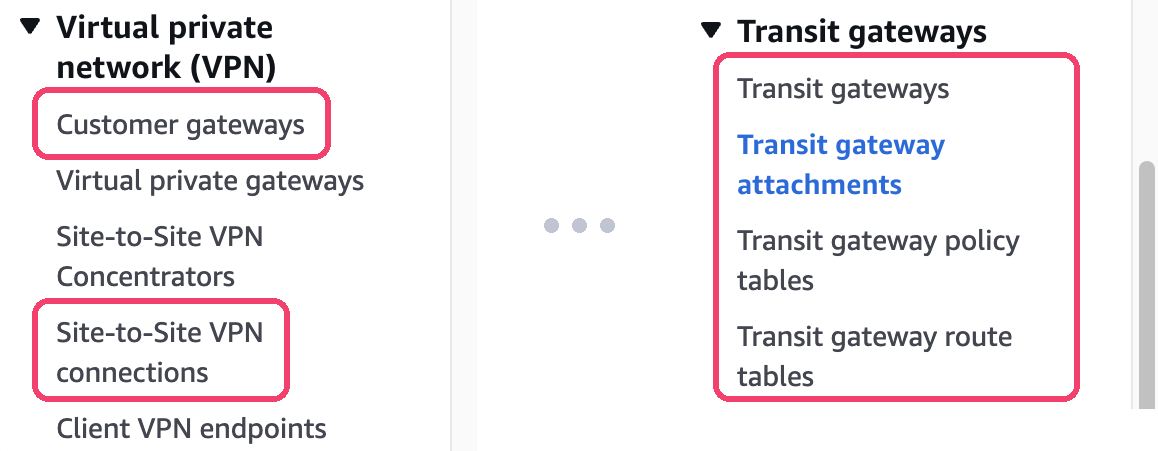
All the AWS pages used below are in the VPC console, in the left menu under Virtual private network (VPN) and Transit gateways.
Step 1: Create a customer gateway
The customer gateway tells AWS where your Vipilink gateway is. If you already created one for this Vipilink gateway, for example on the AWS virtual private gateway page, reuse it and go to Step 2.
-
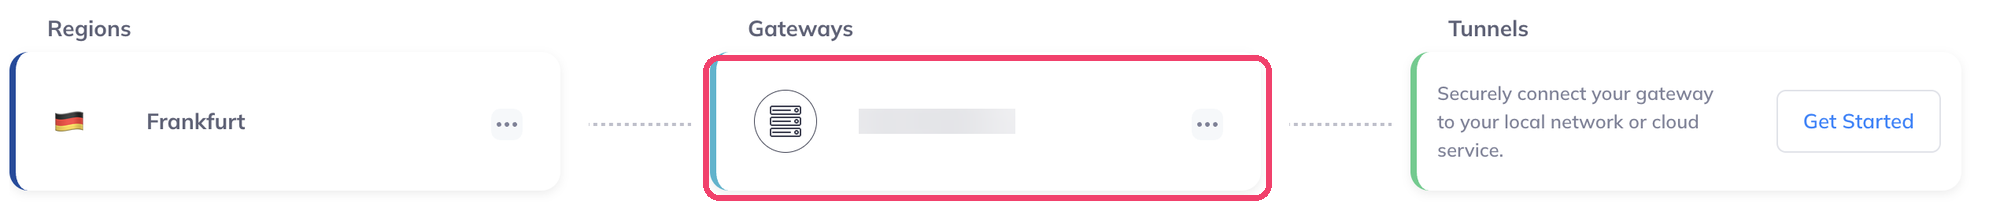
In the Vipilink console, go to Networks → Networks, open your network and copy the public IP shown on the gateway card.
-
In the AWS console, go to Virtual private network (VPN) → Customer gateways and click Create customer gateway.

-
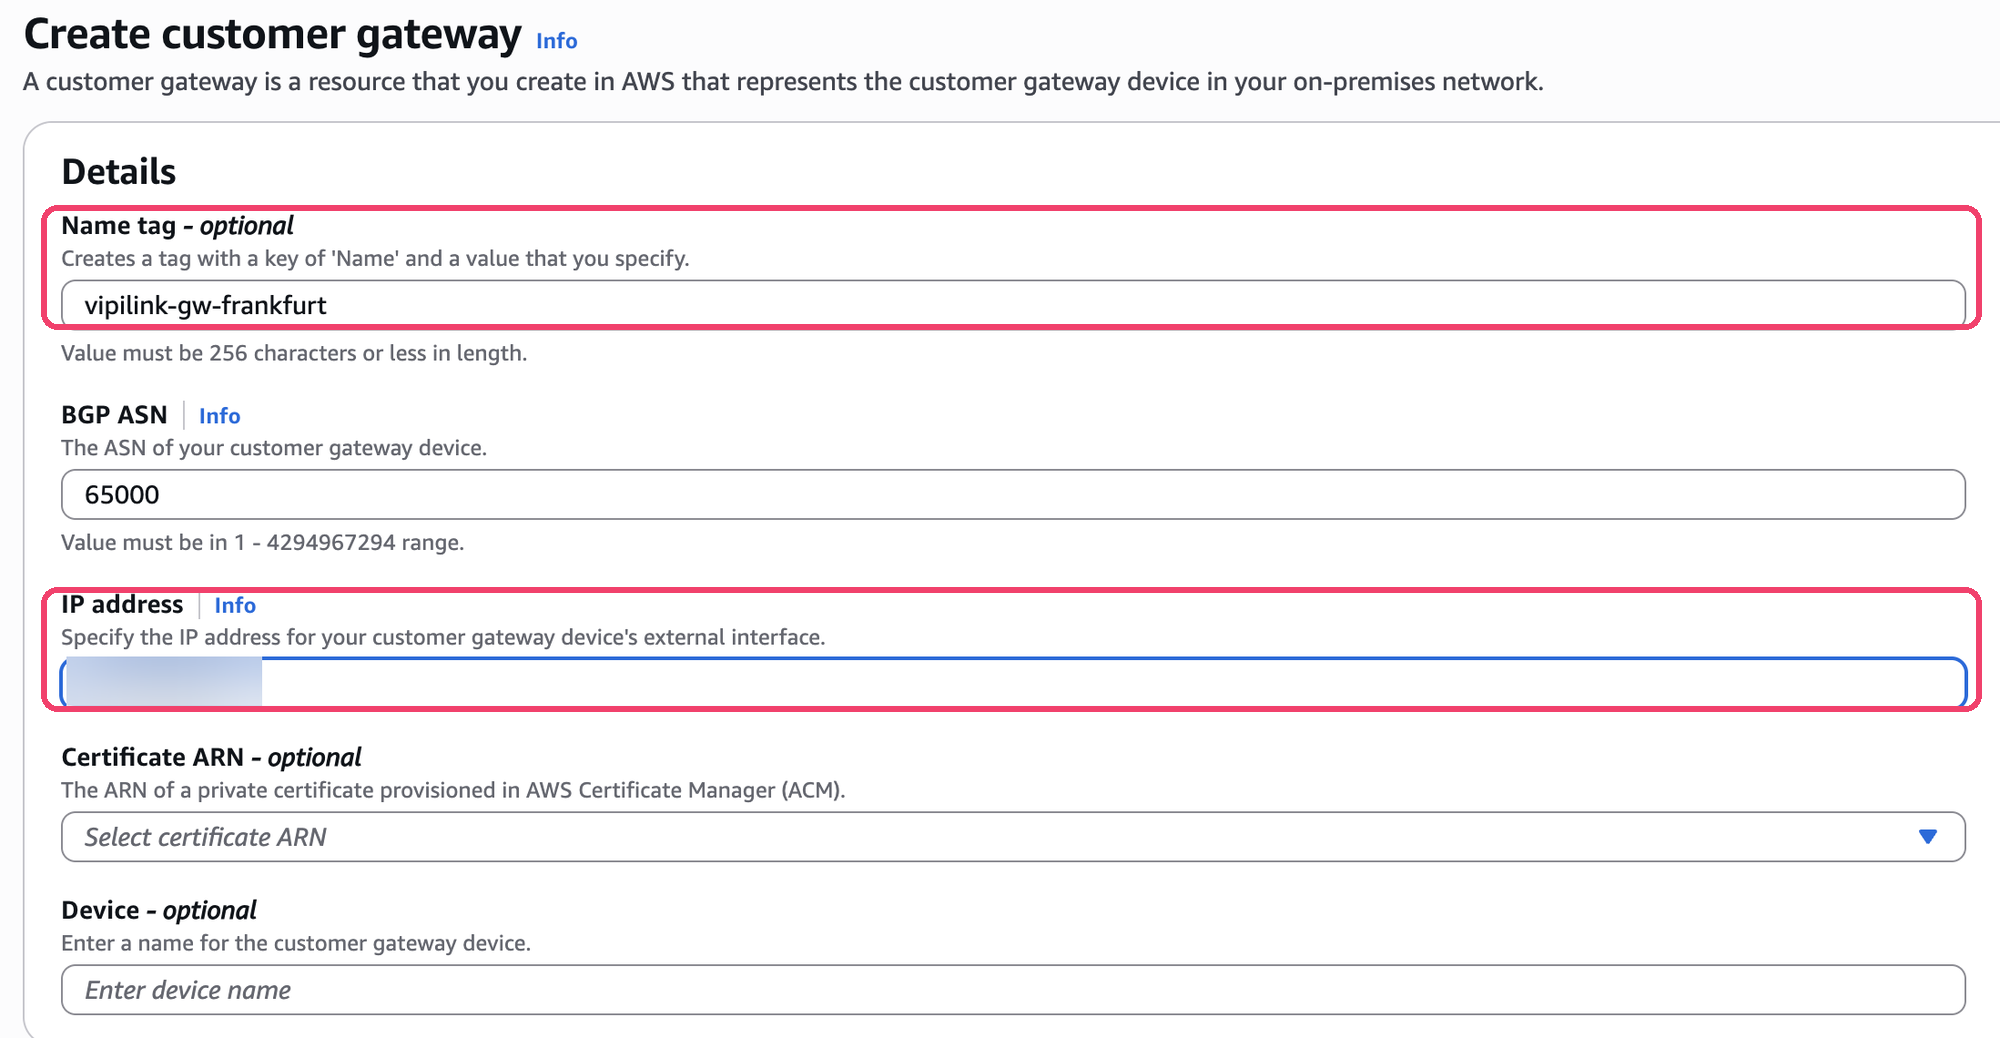
Fill in the form:
Field Value Name tag vipilink-gw-frankfurtBGP ASN Keep the default. It is not used with static routing. IP address The Vipilink gateway public IP you copied -
Click Create customer gateway.
Step 2: Create a transit gateway
-
Go to Transit gateways → Transit gateways and click Create transit gateway.

-
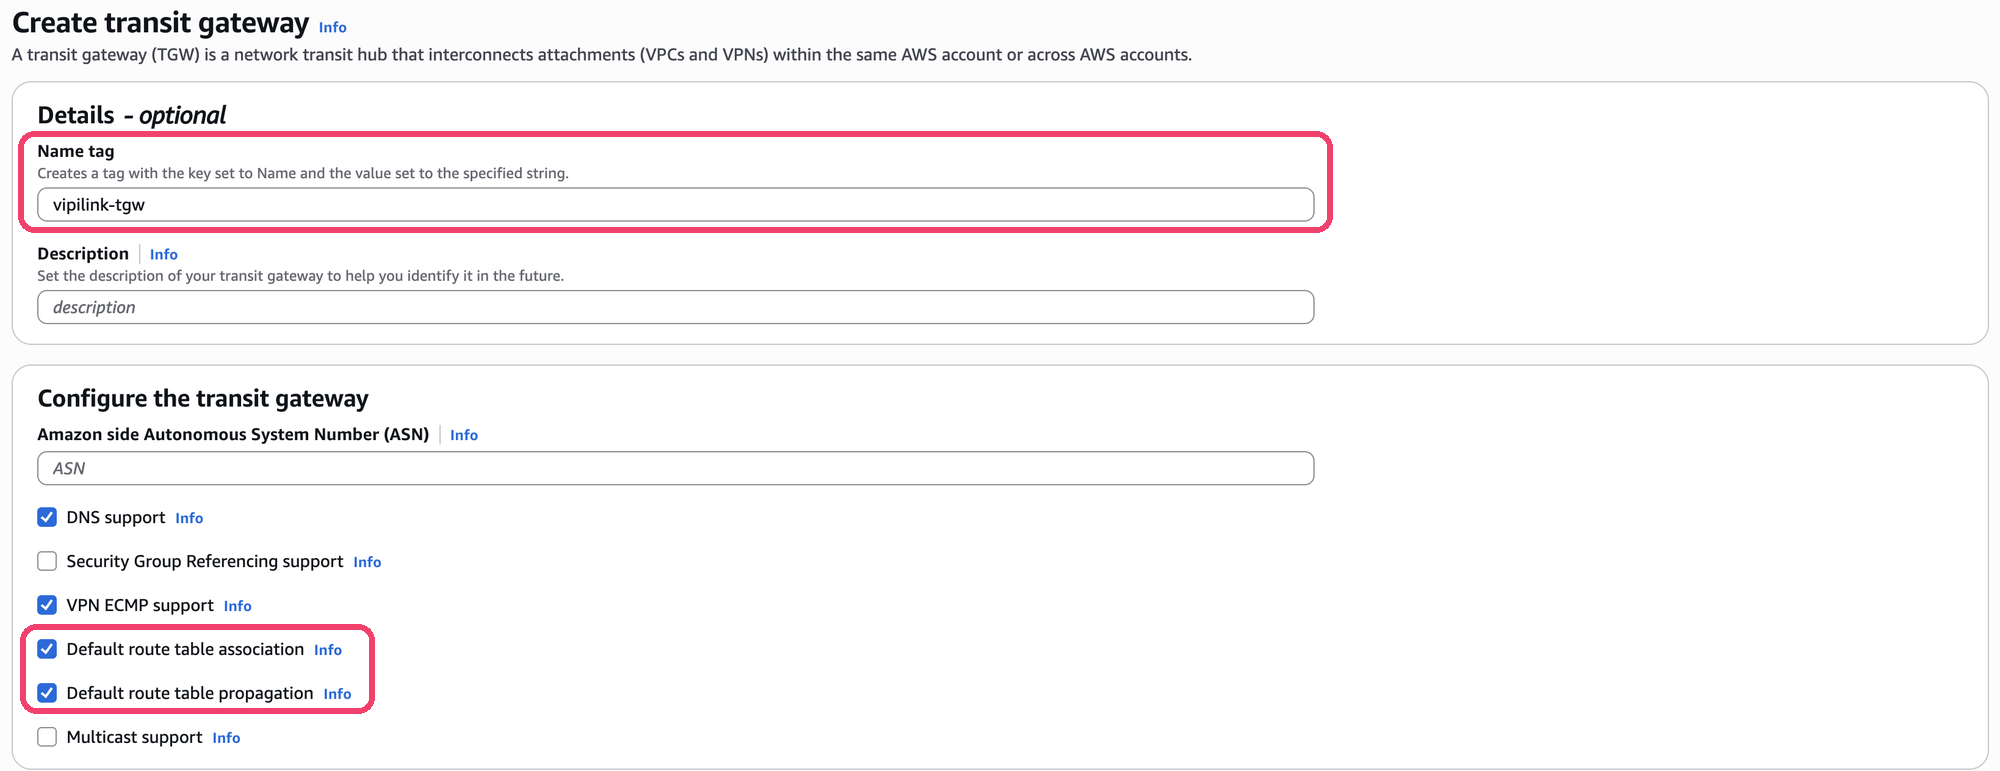
Enter a Name tag, for example
vipilink-tgw. - Keep the other settings at their defaults. Make sure Default route table association and Default route table propagation are selected. With these on, the transit gateway learns your VPC CIDR on its own.
- Click Create transit gateway. Wait until the State changes to Available. This can take a few minutes.
Step 3: Attach your VPC
-
Go to Transit gateways → Transit gateway attachments and click Create transit gateway attachment.

-
Fill in the form:
Field Value Name tag tgw-app-vpcTransit gateway ID vipilink-tgwAttachment type VPC VPC ID Your VPC, for example app-vpcSubnet IDs One subnet in each Availability Zone where you have resources Leave the other fields at their defaults.
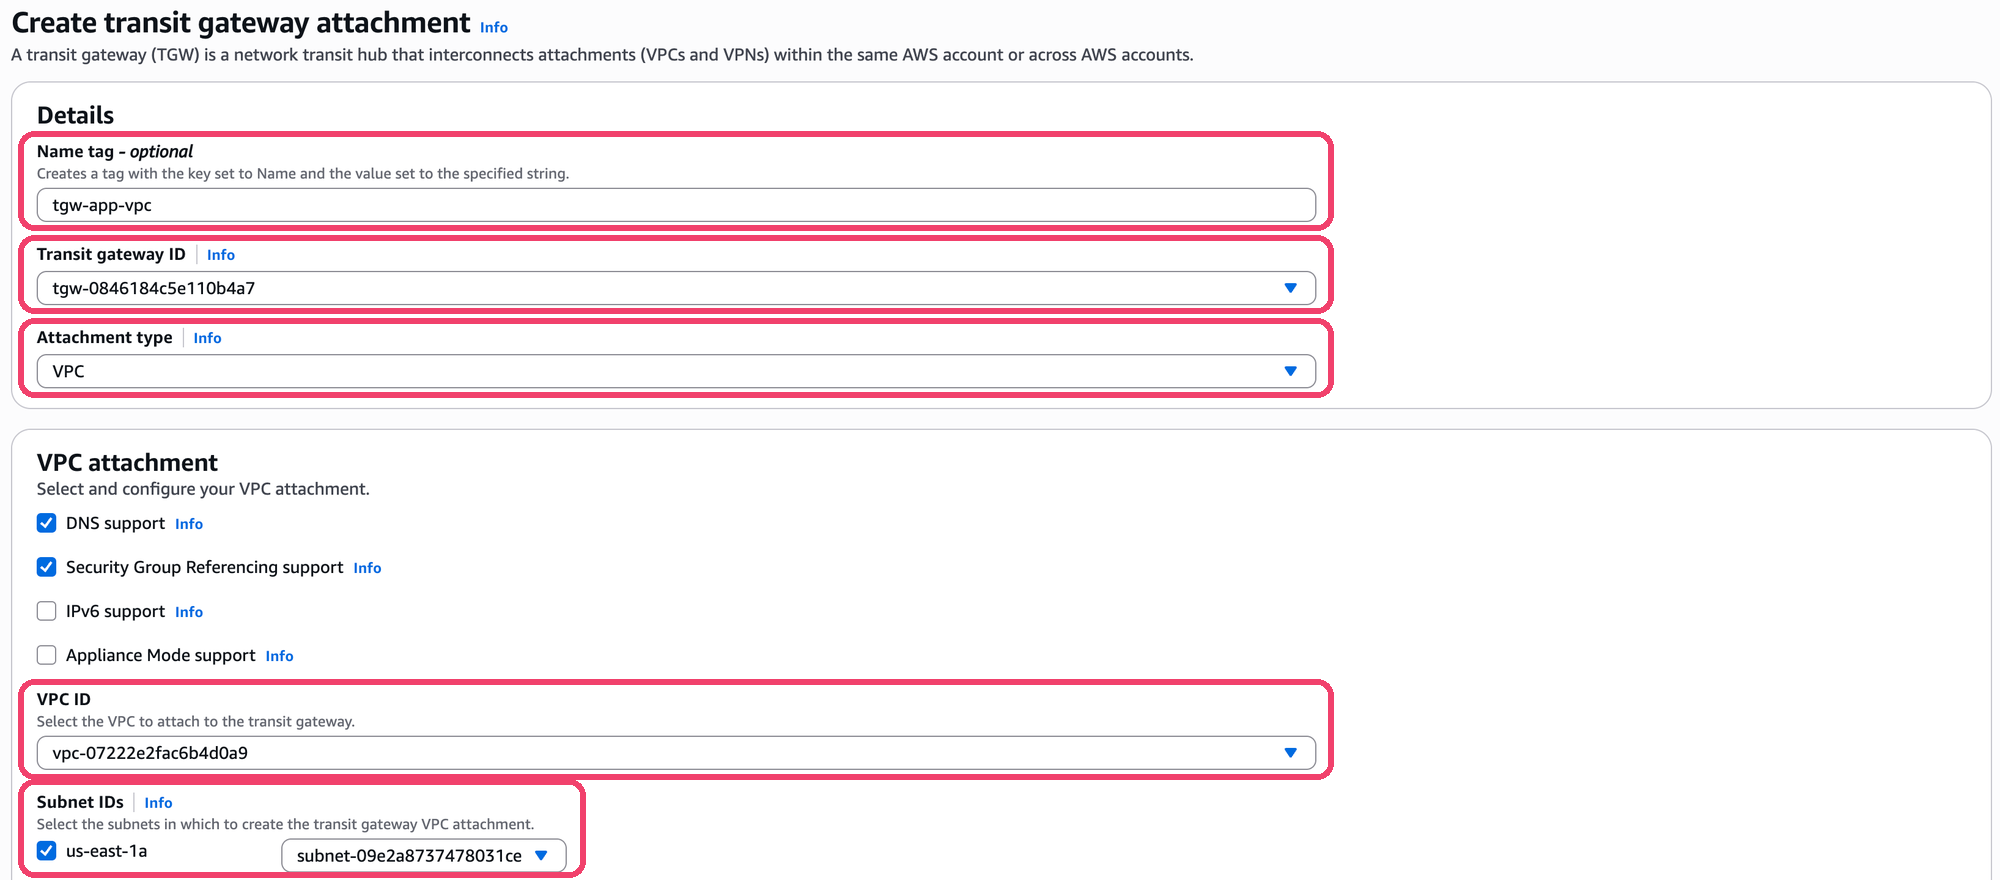
-
Click Create transit gateway attachment.
Choose subnets in every Availability Zone you use
The transit gateway reaches your resources through the subnets you choose here. Resources in an Availability Zone without a selected subnet can't be reached through the tunnel.
To connect more VPCs to Vipilink, repeat this step for each VPC, then add a route for each one in Step 6 and Step 8.
Step 4: Create the VPN attachment
The VPN attachment connects the transit gateway to your Vipilink gateway. When you create it, AWS also creates the Site-to-Site VPN connection for you, so you don't create one separately.
- Go to Transit gateways → Transit gateway attachments and click Create transit gateway attachment again.
-
Fill in the form:
Field Value Transit gateway ID vipilink-tgwAttachment type VPN Customer Gateway Existing Customer Gateway ID vipilink-gw-frankfurtfrom Step 1Routing options Static Leave the other fields, including Tunnel Options, at their defaults. Amazon generates the tunnel addresses and pre-shared keys.
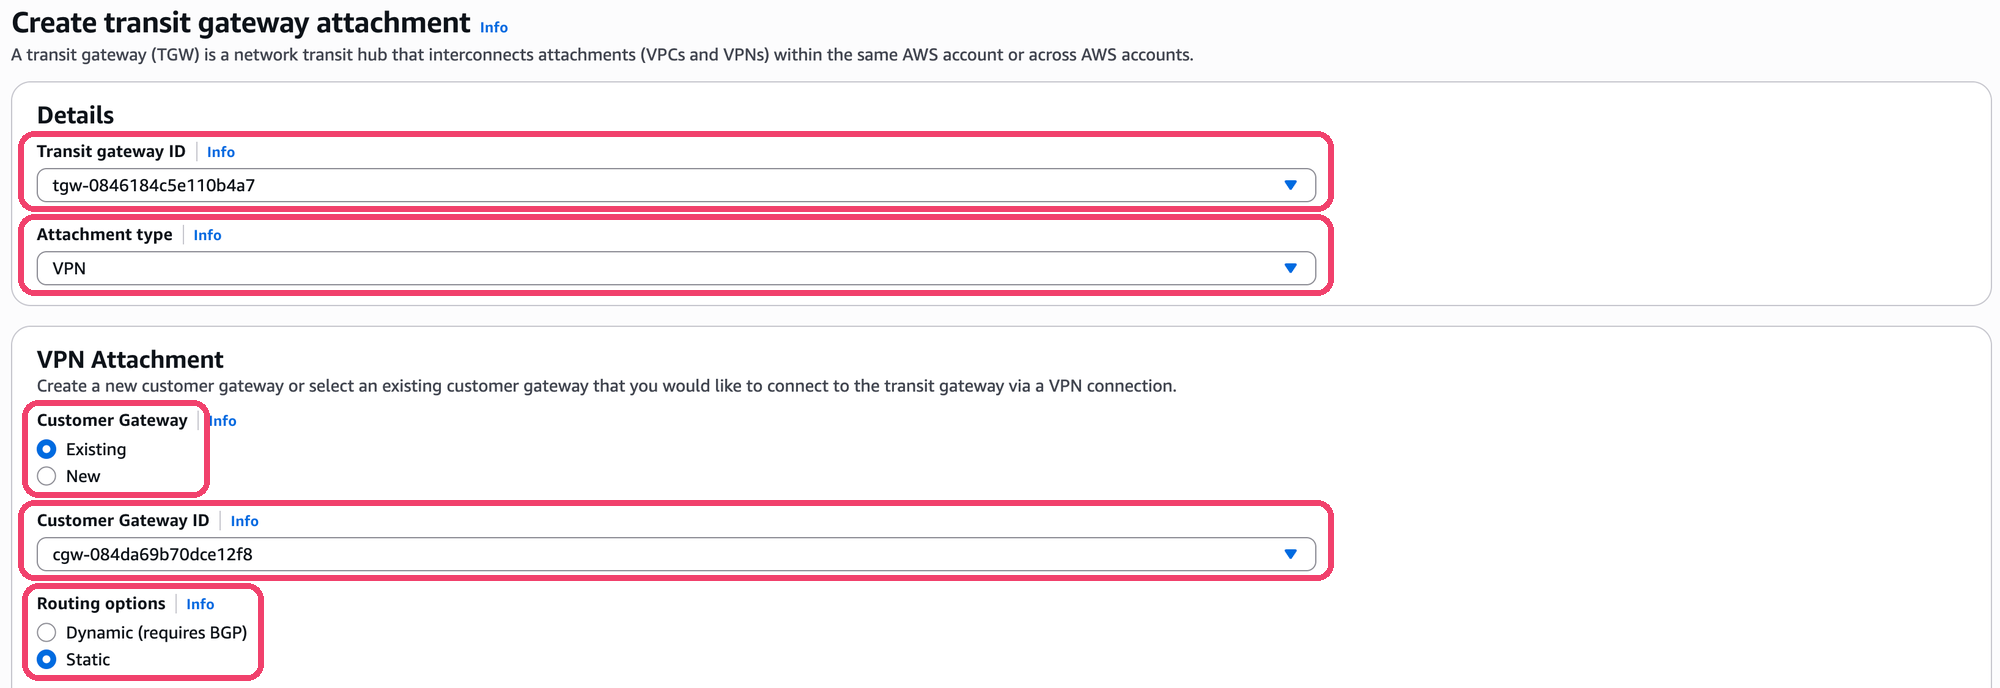
-
Click Create transit gateway attachment.
- The form has no name field. To name the attachment, point to its empty Name cell in the list, click the pencil icon and enter
vipilink-tgw-vpn-frankfurt. - Wait until both attachments show Available. This can take a few minutes. The VPN attachment's Resource ID starts with
vpn-. This is the VPN connection AWS created for you.

Step 5: Name the VPN connection and download its configuration
Vipilink reads the configuration file and fills in the tunnel settings for you.
- Go to Virtual private network (VPN) → Site-to-Site VPN connections. The new connection shows your transit gateway in the Transit gateway column.
- Name it: point to its empty Name cell, click the pencil icon and enter
vipilink-vpn-frankfurt. -
Select the connection (1) and click Download configuration (2).

-
Choose these options and click Download:
Field Value Vendor Generic Platform Generic Software Vendor Agnostic IKE version ikev2 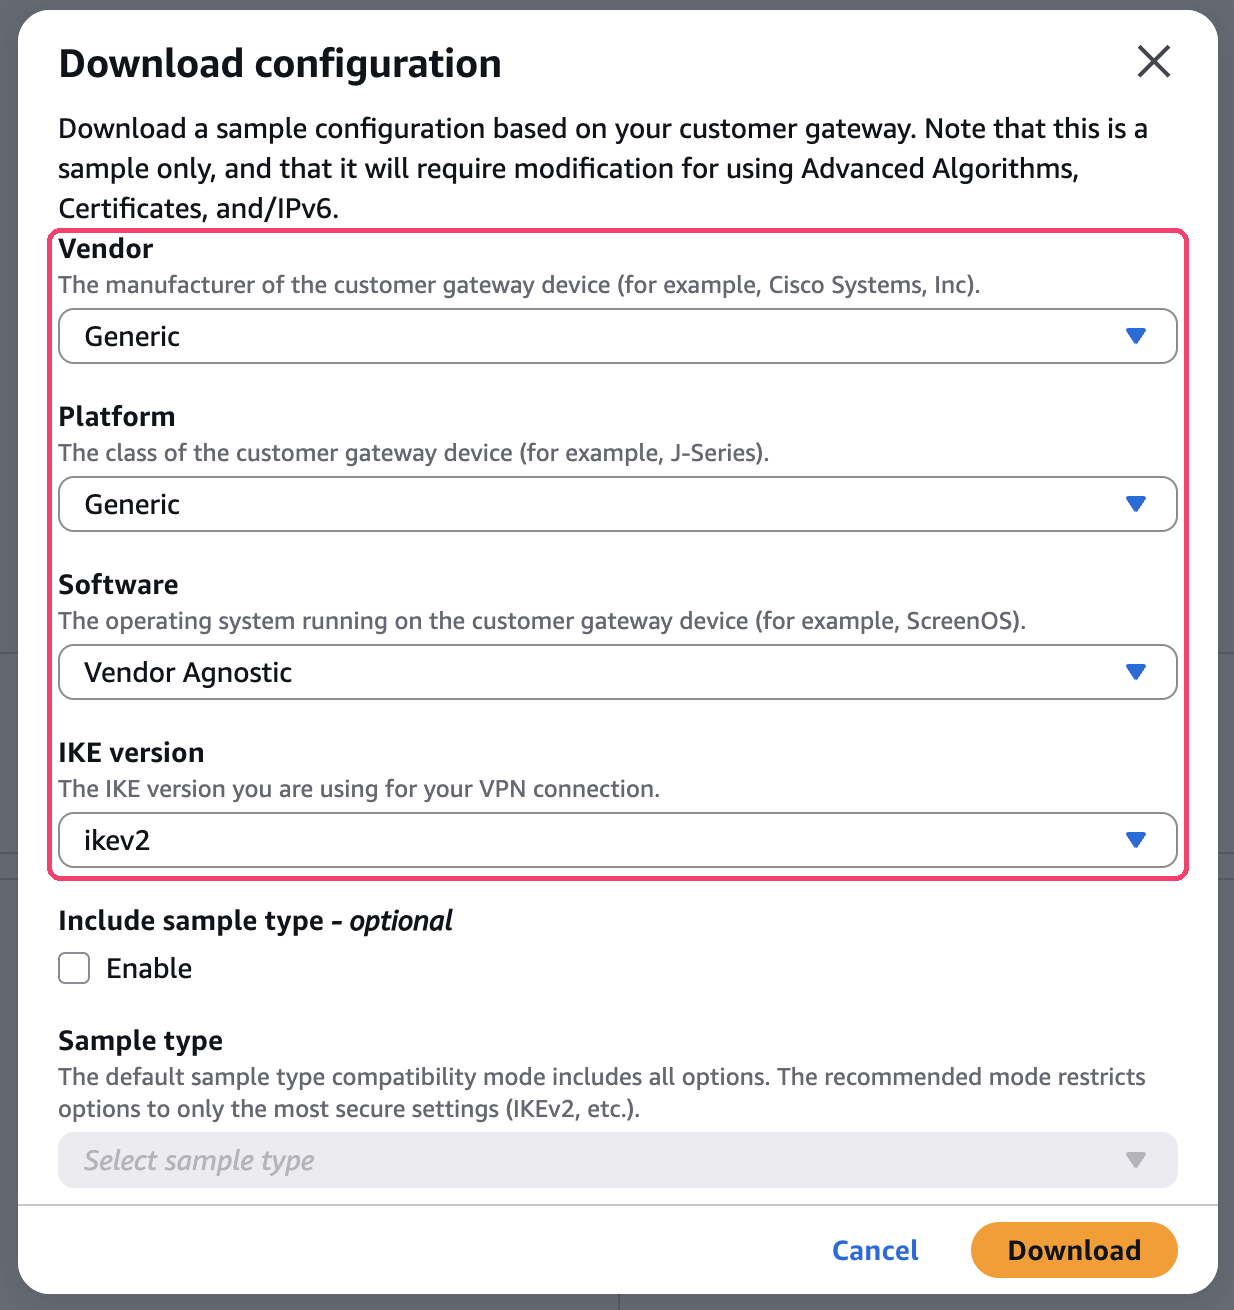
Keep the file private
The configuration file contains the tunnel pre-shared keys. Store it somewhere safe and delete it when you are done.
Step 6: Add the routes in AWS
Traffic needs a route in two places on the AWS side: in the transit gateway, and in your VPC.
In the transit gateway
The transit gateway already knows your VPC CIDR, because the VPC attachment propagates it. It doesn't know the Vipilink subnet yet, because static VPN attachments don't propagate routes. Add it yourself:
-
Go to Transit gateways → Transit gateway route tables (1), select the route table of your transit gateway (2), open the Routes tab (3) and click Create static route (4).

-
Fill in the form:
- CIDR: your Vipilink network subnet, for example
10.13.0.0/16 - Type: Active
- Choose attachment: the VPN attachment,
vipilink-tgw-vpn-frankfurt
- CIDR: your Vipilink network subnet, for example
- Click Create static route.
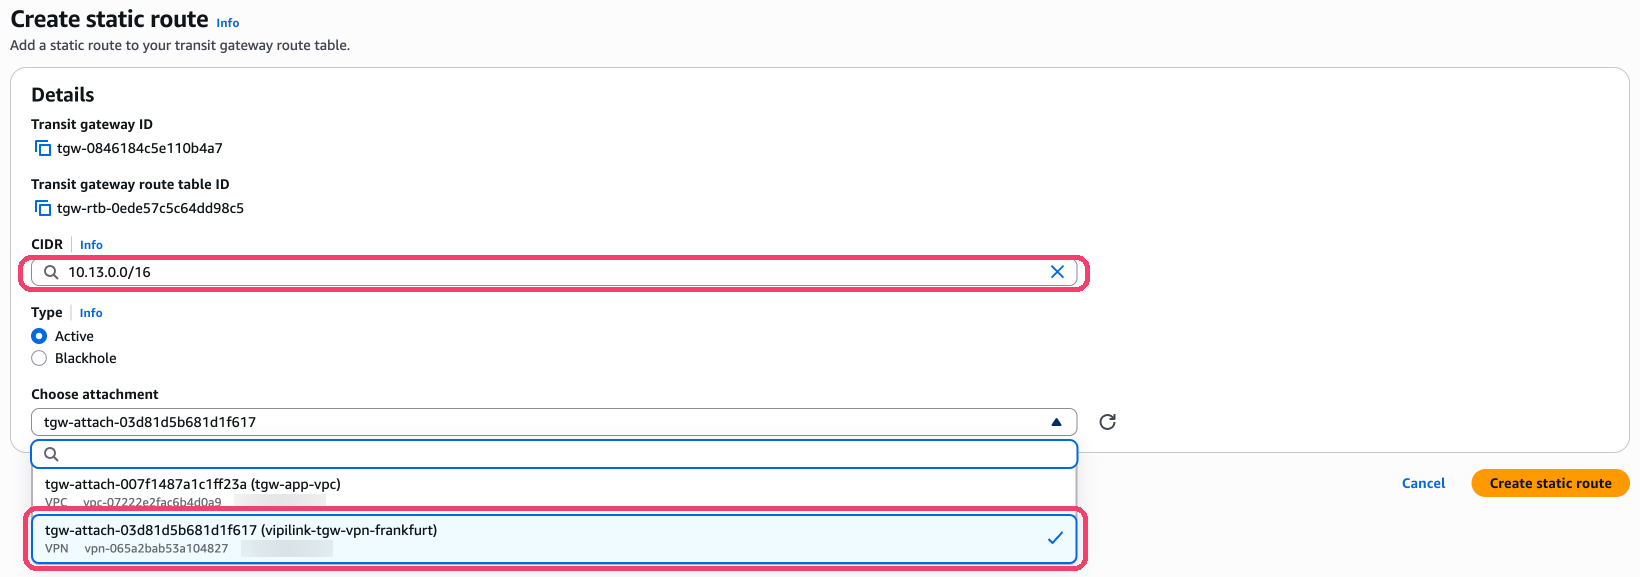
The route shows Blackhole at first
Until the tunnel is up, the Route state of the new route shows Blackhole, even though you chose Active. This is expected. AWS drops traffic for a VPN route while none of its tunnels are up. The state changes to Active on its own after you add the tunnel in Vipilink in Step 7.
When the tunnel is up, the route table has both routes:

In the VPC
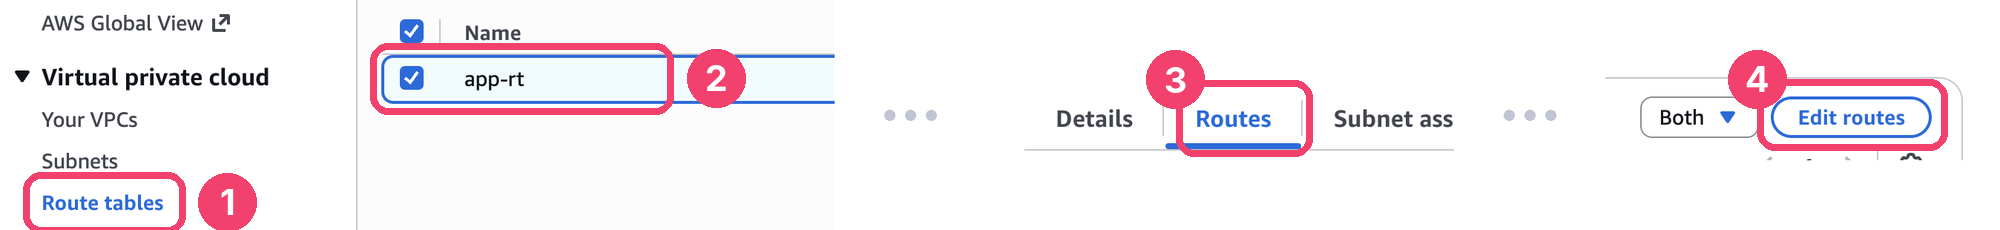
- Go to Virtual private cloud → Route tables (1) and select the route table used by your VPC subnets (2).
-
Open the Routes tab (3) and click Edit routes (4).
-
Click Add route:
- Destination: your Vipilink network subnet, for example
10.13.0.0/16 - Target: Transit Gateway, then choose
vipilink-tgw
- Destination: your Vipilink network subnet, for example
- Click Save changes.
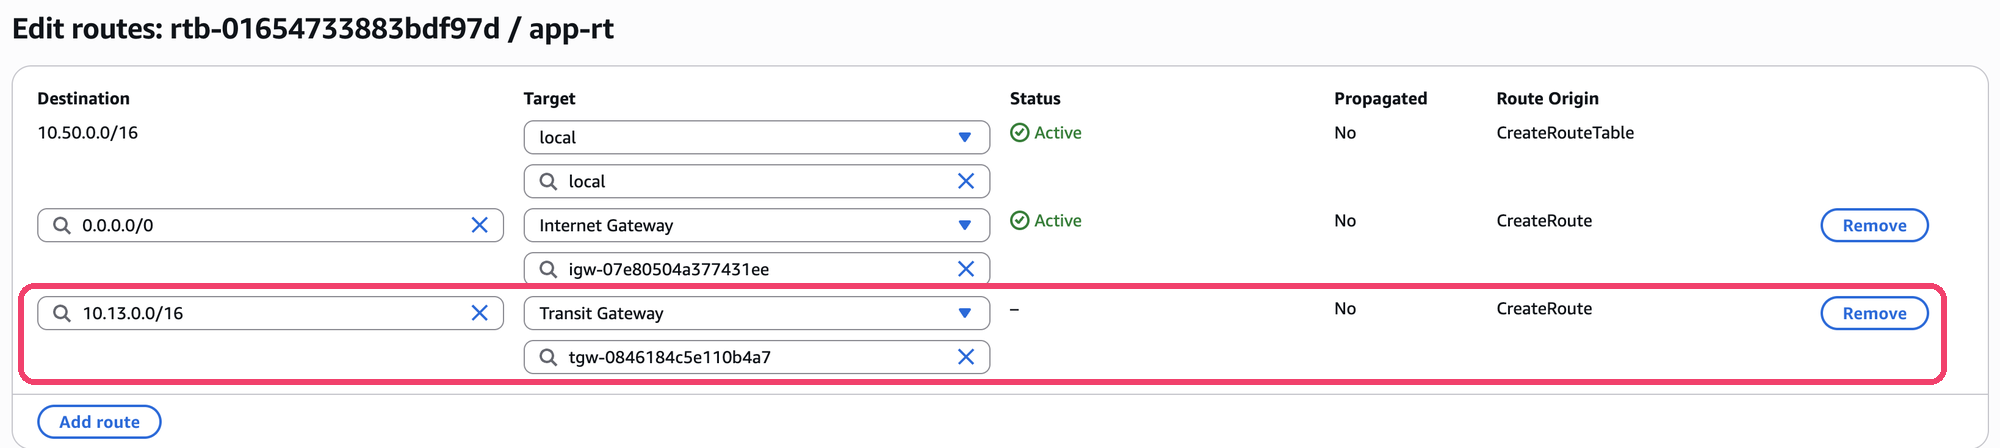
If your VPC subnets use more than one route table, add the route to each of them.
Step 7: Add the tunnel in Vipilink
-
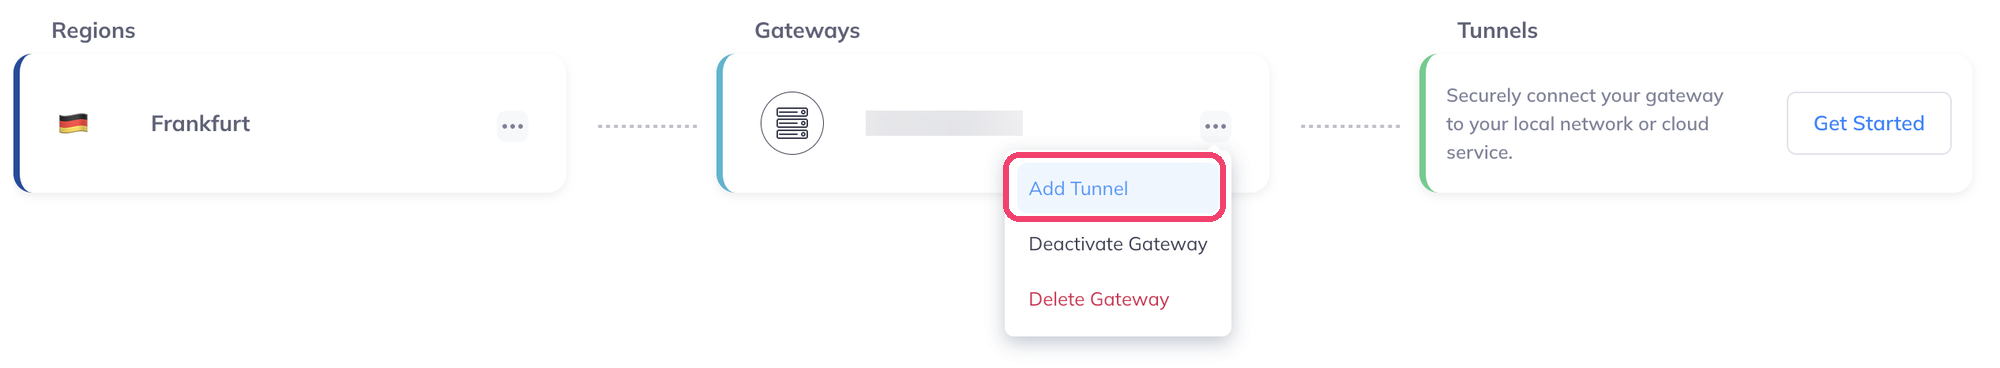
In the Vipilink console, open your network. On the gateway card, click the ... menu and choose Add Tunnel.
-
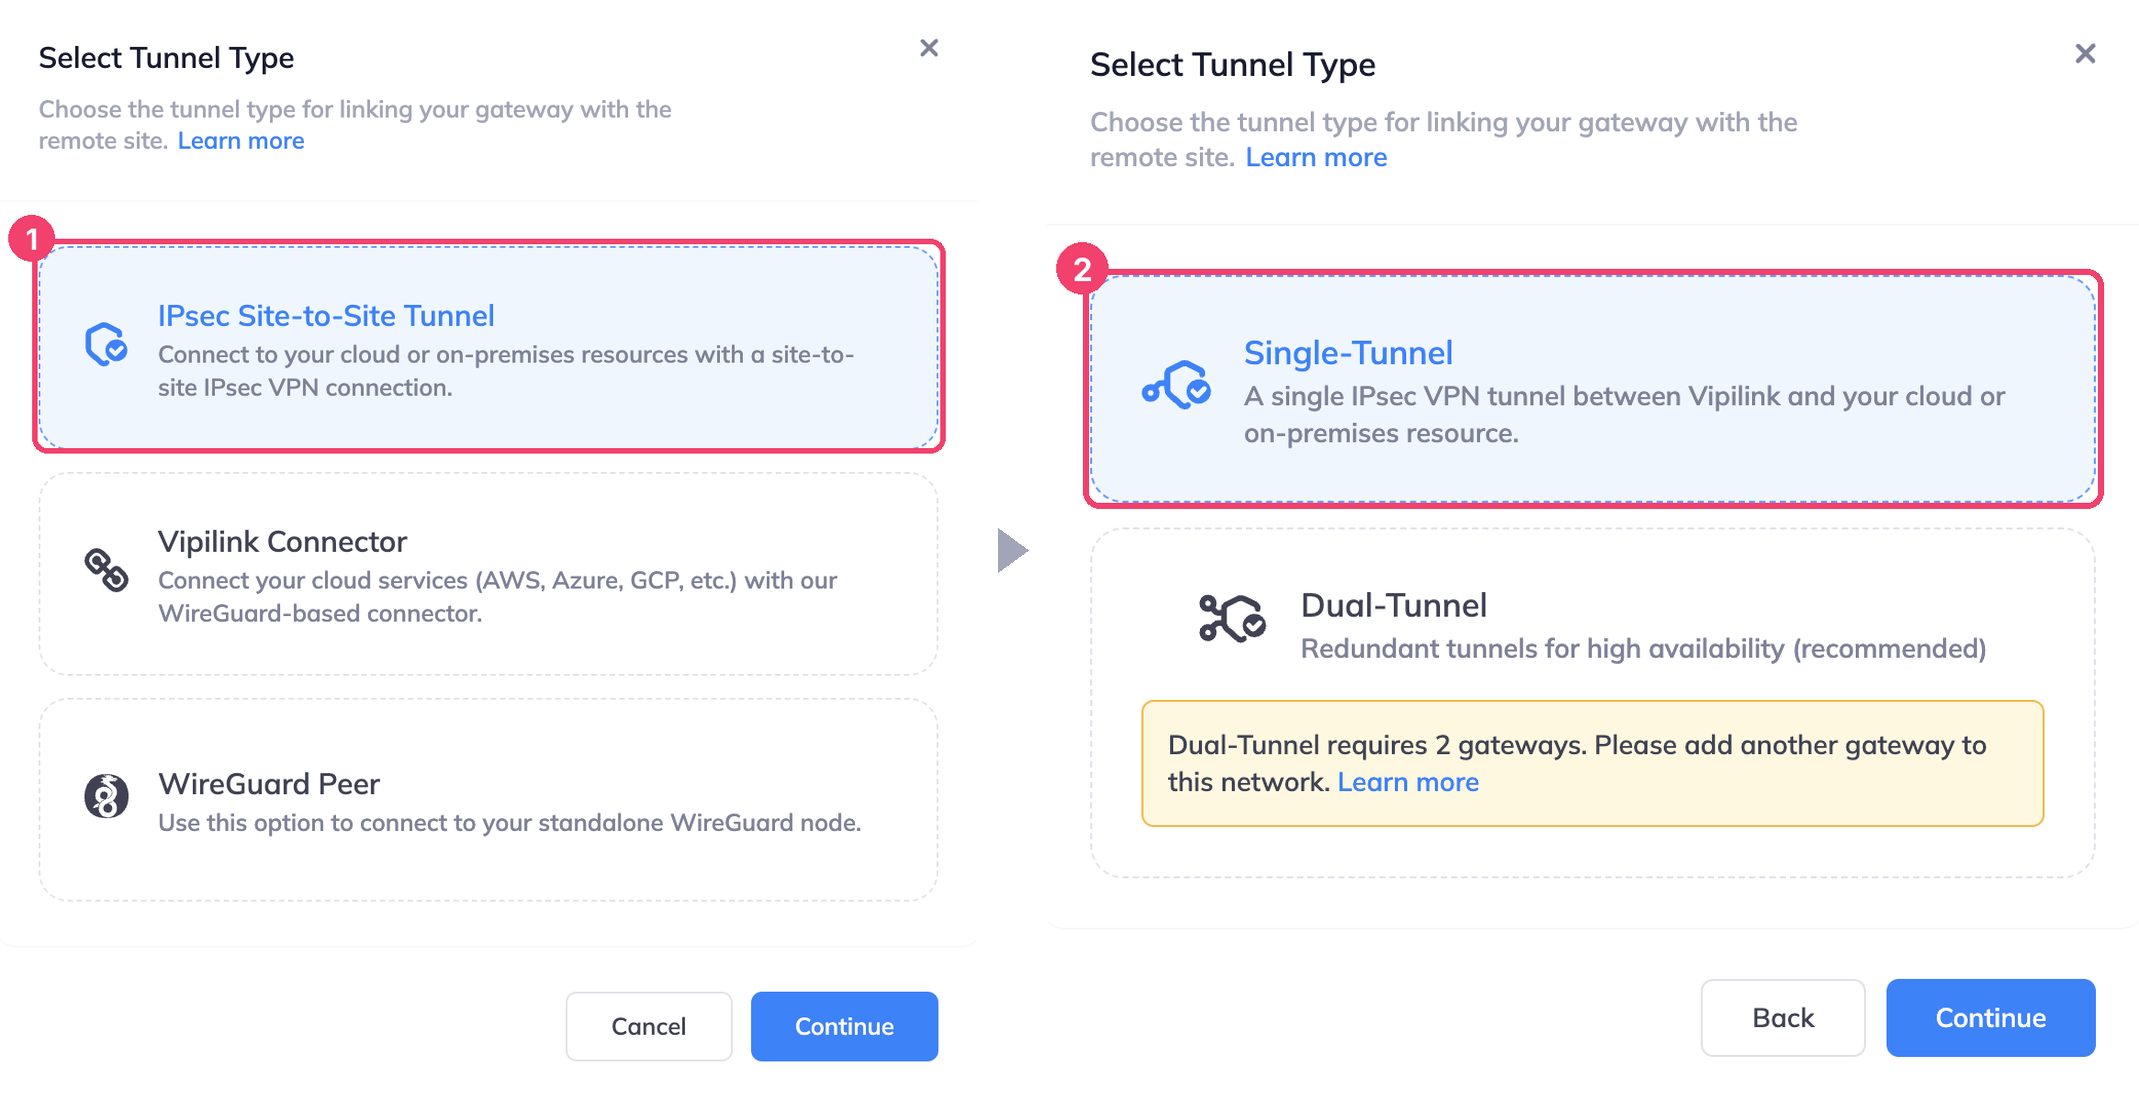
Choose IPsec Site-to-Site Tunnel (1) and click Continue. Then choose Single-Tunnel (2) and click Continue.
-
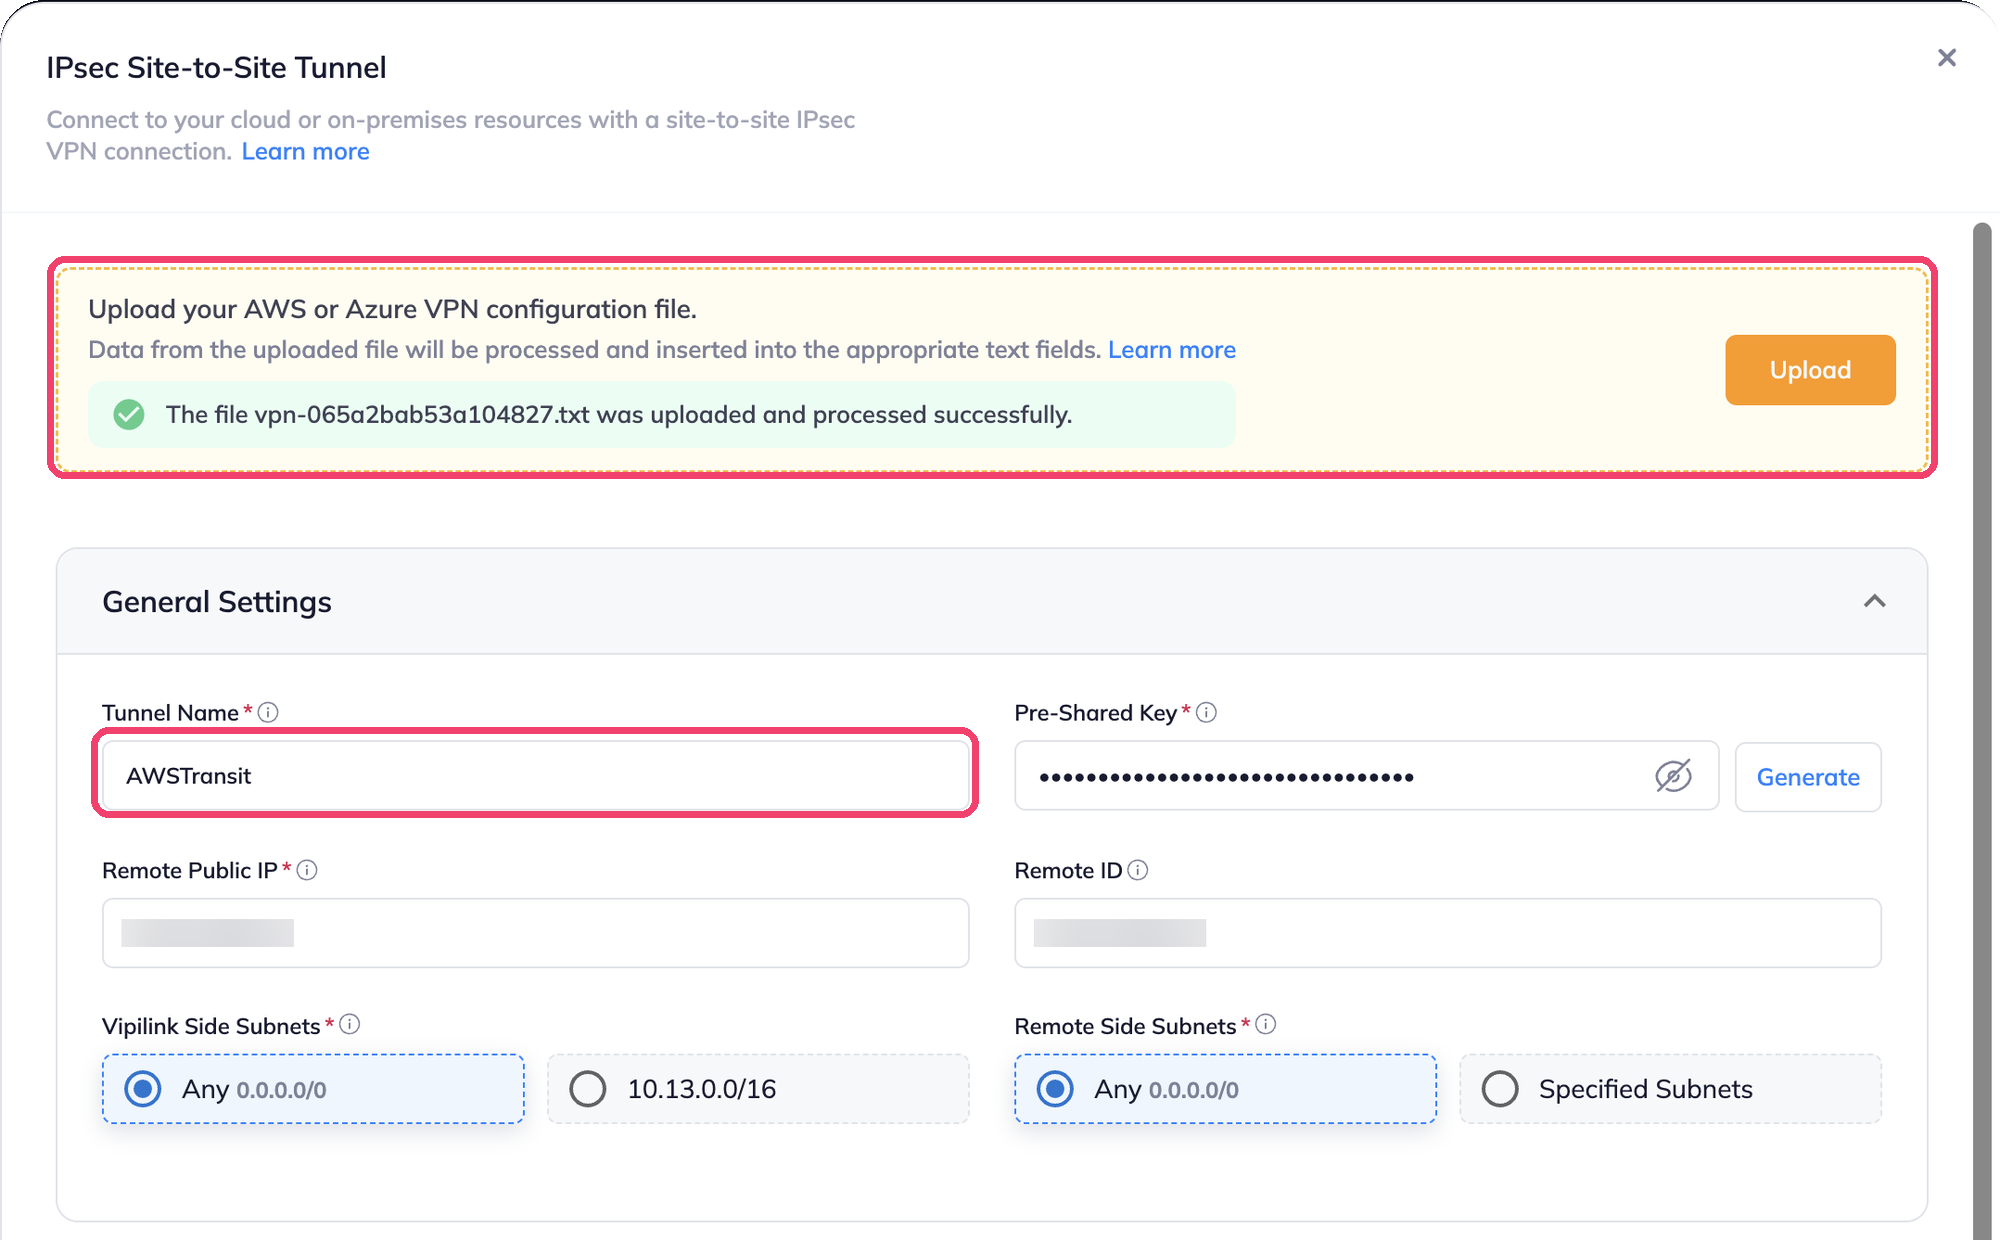
Click Upload and select the configuration file from Step 5. Vipilink fills in Pre-Shared Key, Remote Public IP and Remote ID.
- Enter a Tunnel Name, for example
AWSTransit. Use letters and numbers only. -
Keep Vipilink Side Subnets and Remote Side Subnets set to Any.
-
Keep the Advanced Settings defaults. AWS accepts them:
Setting Value IKE Version V2 IKE Lifetime 8h Tunnel Lifetime 1h Dead Peer Detection Delay / Timeout 10s / 30s Encryption (Phase 1 and 2) aes256 Integrity (Phase 1 and 2) sha256 Diffie-Hellman Groups (Phase 1 and 2) 14 -
Click Add Tunnel.
Step 8: Route Vipilink traffic to the VPC
Tell Vipilink which subnets are behind the tunnel.
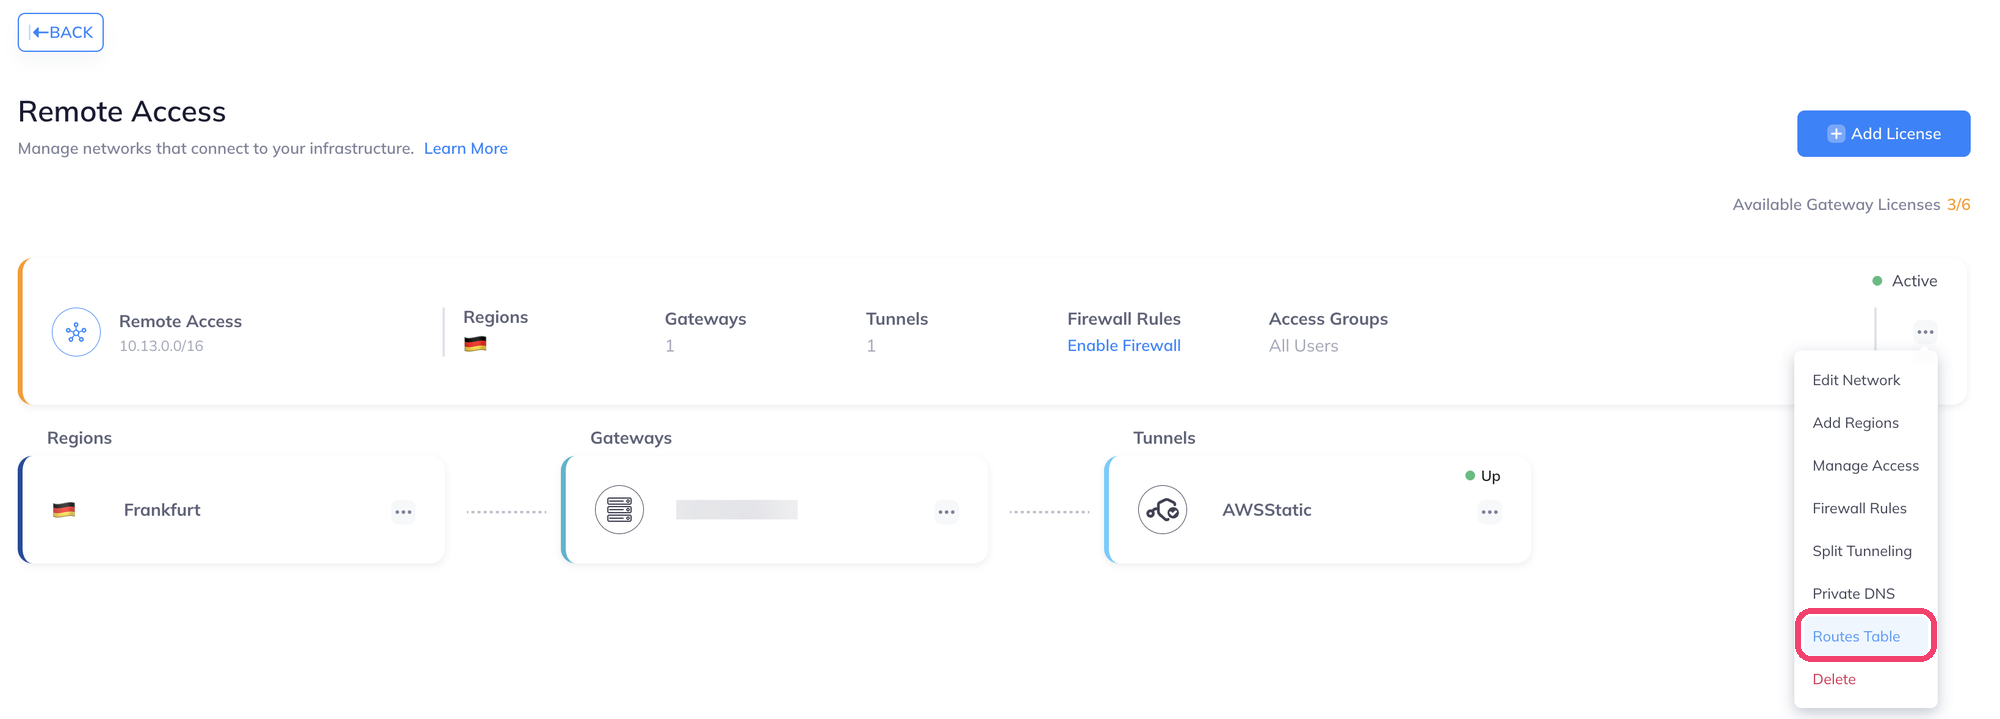
-
On the network card, click the ... menu and choose Route Table.
-
Click Add Routes, choose your tunnel, enter the VPC CIDR (for example
10.50.0.0/16) and click Add Routes. If you attached more VPCs in Step 3, enter each VPC CIDR.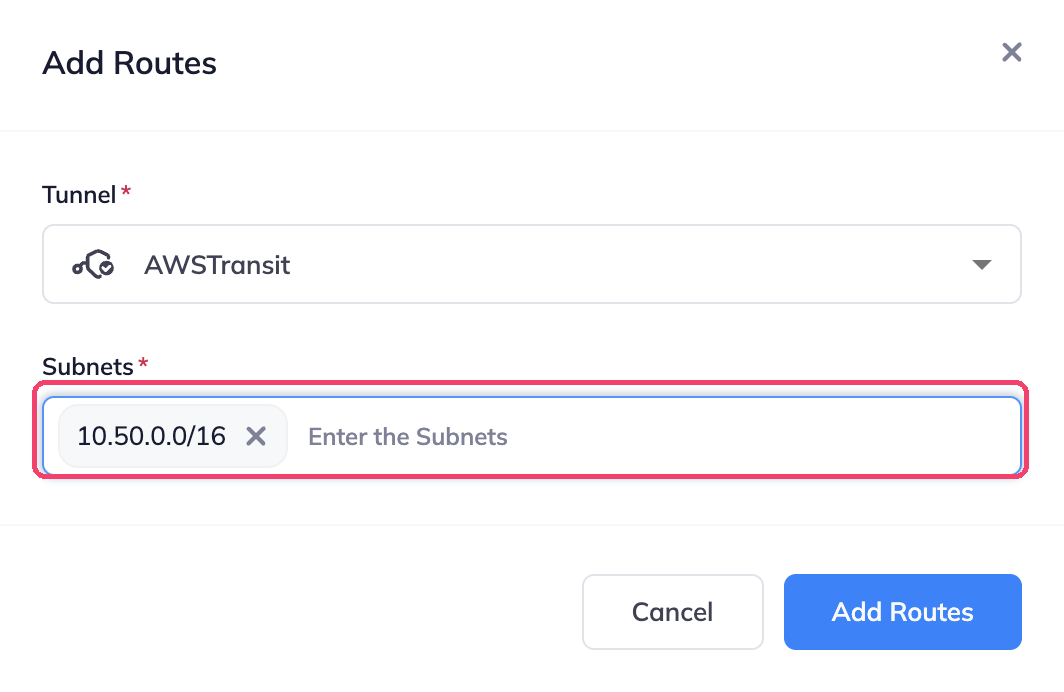
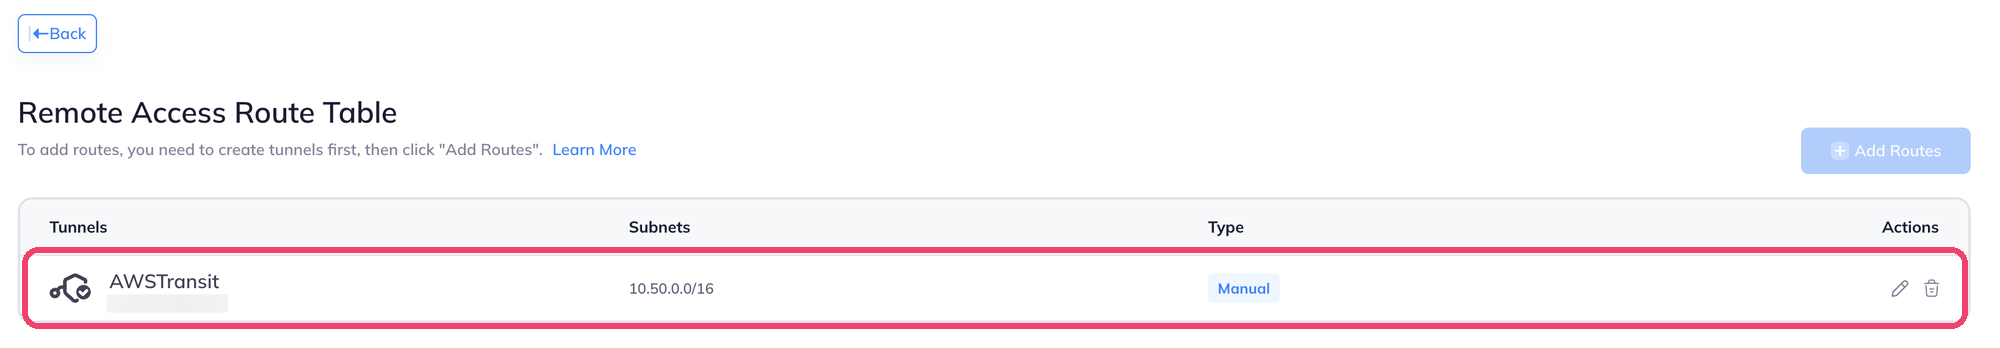
-
The route appears in the table with the type Manual.
Step 9: Check the connection
-
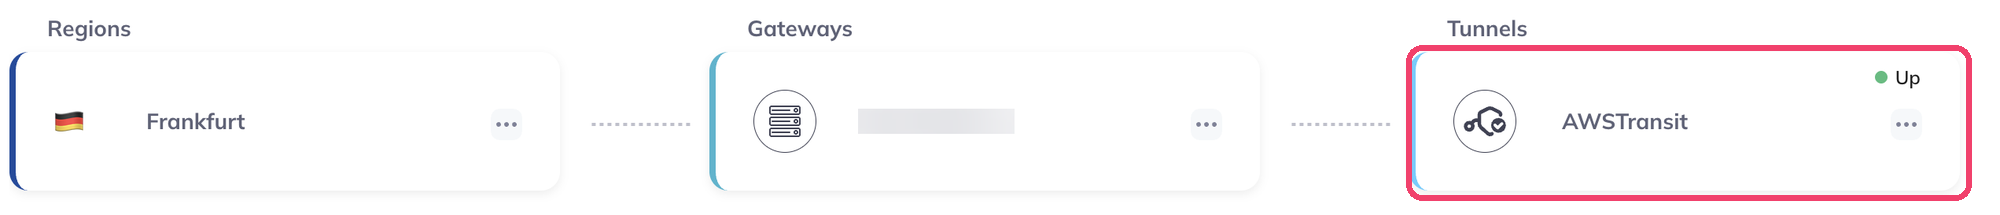
In the Vipilink console, the tunnel card shows Up.
-
In the AWS console, select the VPN connection and open Tunnel details. Tunnel 1 shows Up.

Tunnel 2 shows Down
This is expected. AWS creates two tunnels for every VPN connection, and a single-tunnel setup uses one of them. AWS also shows a banner saying the connection is not using both tunnels. If you need redundancy, use AWS transit gateway with redundant tunnels.
-
In the transit gateway route table, the route to your Vipilink subnet now shows Active (see Step 6).
-
Connect a device to the network with the Vipilink agent and reach a resource in the VPC, for example with
pingor SSH to a private IP.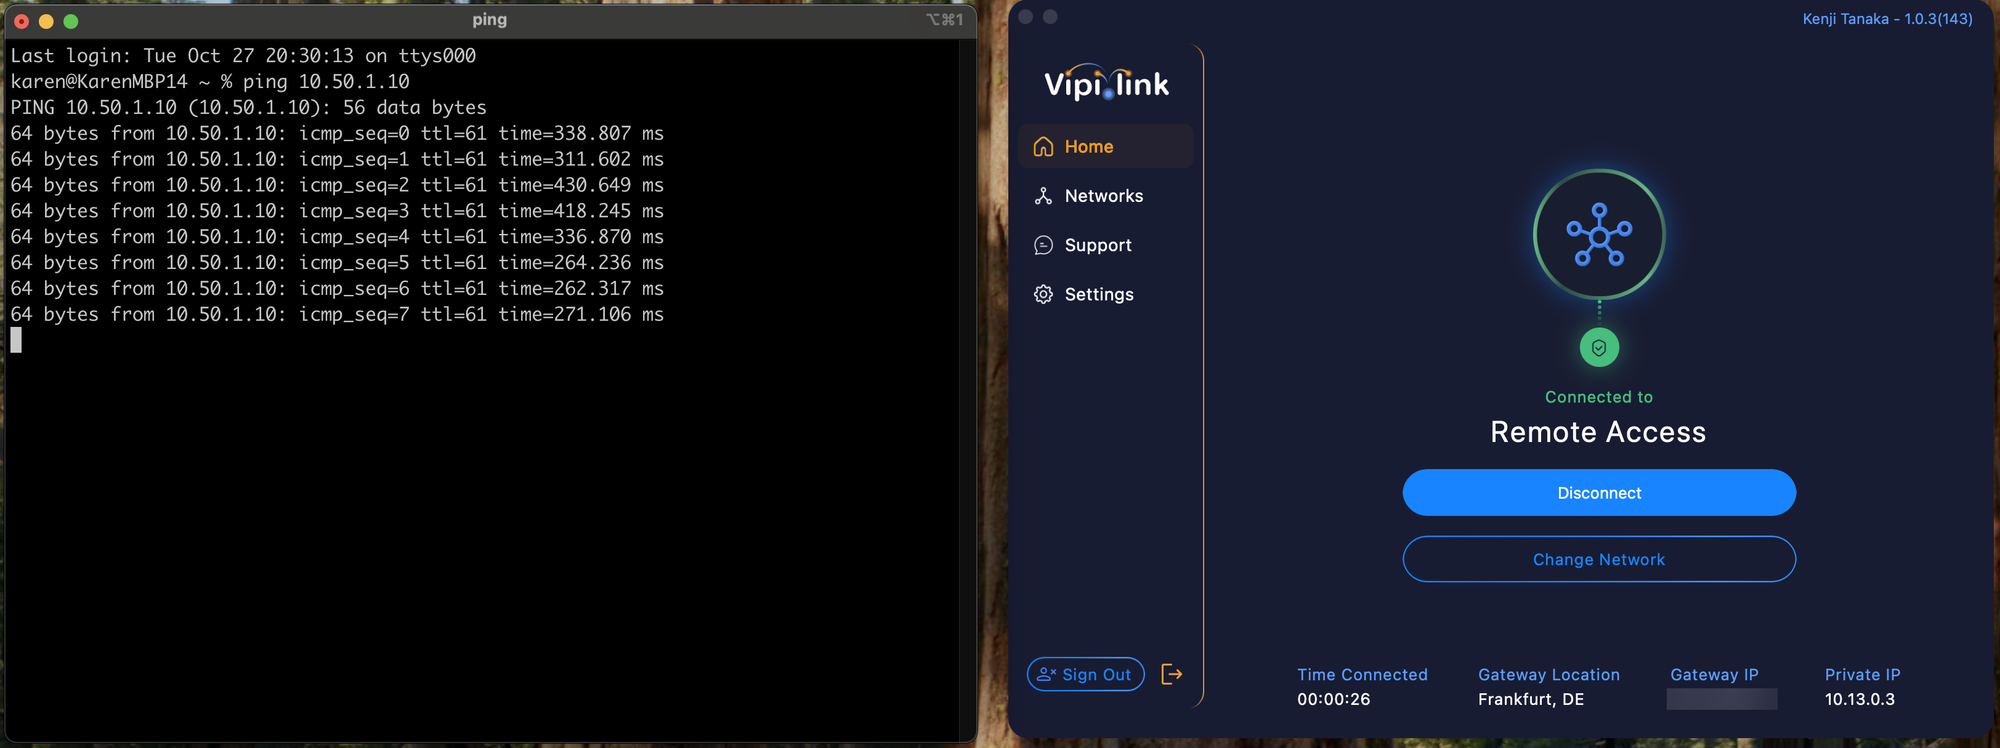
Troubleshooting
| Problem | What to check |
|---|---|
| Tunnel stays Down | The customer gateway IP matches the Vipilink gateway public IP. The file you uploaded belongs to this VPN connection. |
| Transit gateway route stays Blackhole | The tunnel isn't up yet. Fix the tunnel first, and the route turns Active on its own. |
| Tunnel is Up but nothing responds | All three routes exist: the transit gateway static route and the VPC route (Step 6), and the Vipilink route (Step 8). The VPC attachment has a subnet in the Availability Zone of your resource. Security groups and network ACLs in AWS allow traffic from the Vipilink network subnet. Vipilink firewall rules allow the traffic. |