AWS virtual private gateway with redundant tunnels
Connect a Vipilink network to an Amazon VPC with two IPsec tunnels, one from each of two Vipilink gateways to the same AWS virtual private gateway. If one tunnel or gateway goes down, traffic keeps flowing through the other.
BGP runs over the tunnels for redundancy and failover. You still add static routes on both sides, as shown in Step 5 and Step 7.
Before you start
- A Vipilink network with two active gateways. They can be in different regions, for example New Jersey and Miami.
- An Amazon VPC, and permission to create VPN resources in it.
- The Vipilink network subnet and the VPC CIDR must not overlap.
For a setup with one gateway, see AWS virtual private gateway.
Example used on this page
| Item | Example value |
|---|---|
| Vipilink network | Cloud, subnet 10.14.0.0/16 |
| Vipilink gateways | New Jersey and Miami |
| AWS Region | US East (N. Virginia) |
| Amazon VPC | app-vpc, CIDR 10.50.0.0/16 |
AWS resources created for the Vipilink connection get names that start with vipilink-. You create one customer gateway and one VPN connection for each Vipilink gateway.
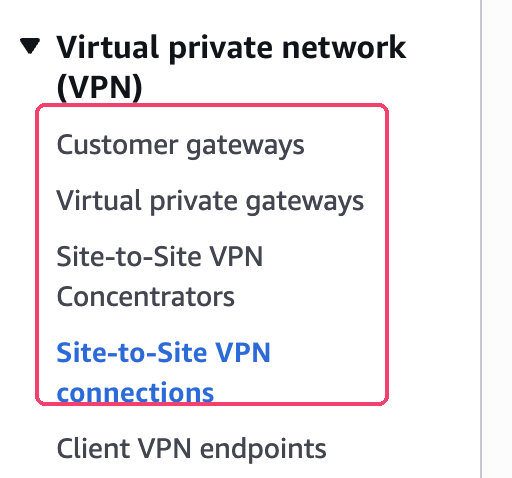
All the AWS pages used below are in the VPC console, in the left menu under Virtual private network (VPN).
Step 1: Create and attach a virtual private gateway
If you already have a virtual private gateway attached to your VPC, you can use it and skip this step.
- In the AWS console, open VPC and go to Virtual private network (VPN) → Virtual private gateways.
-
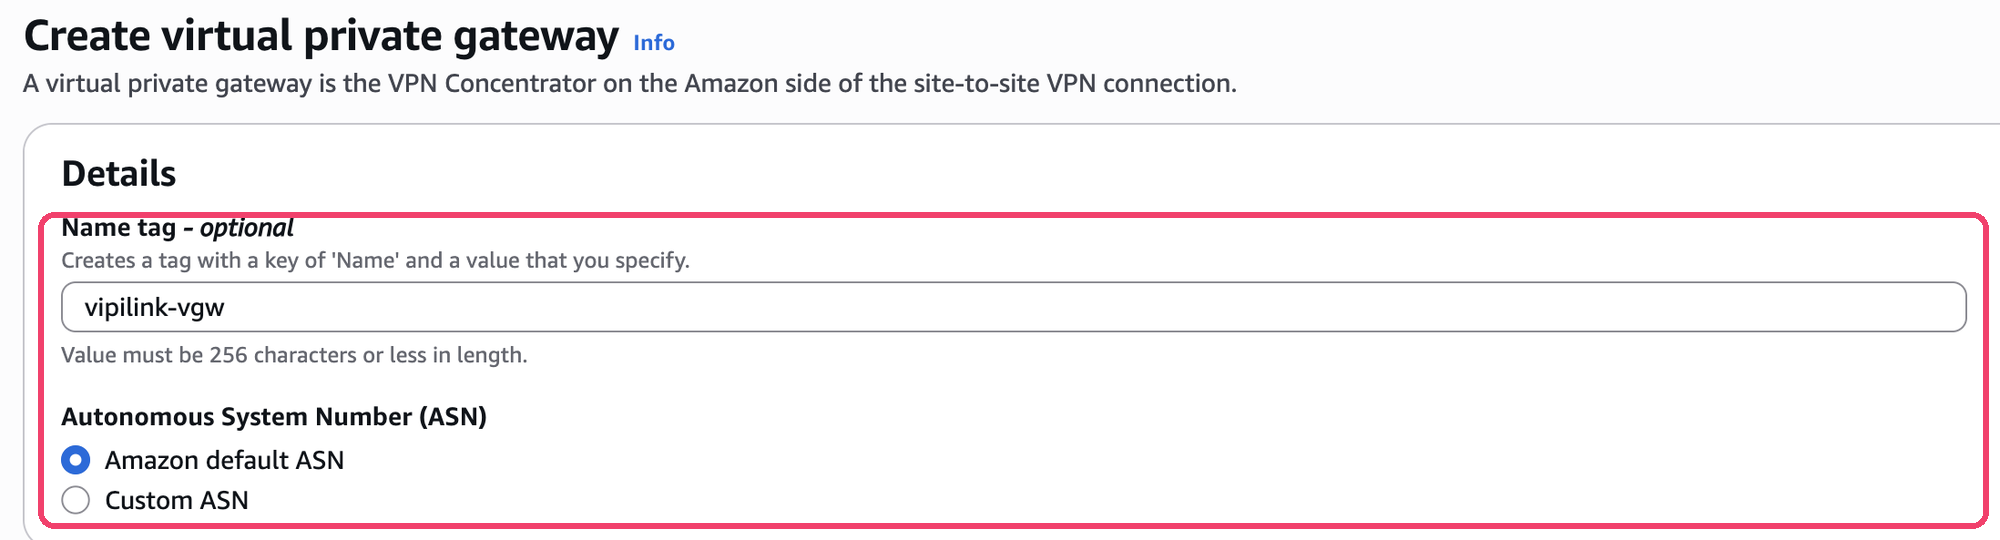
Click Create virtual private gateway, enter a Name tag such as
vipilink-vgw, keep Amazon default ASN and click Create virtual private gateway.
-
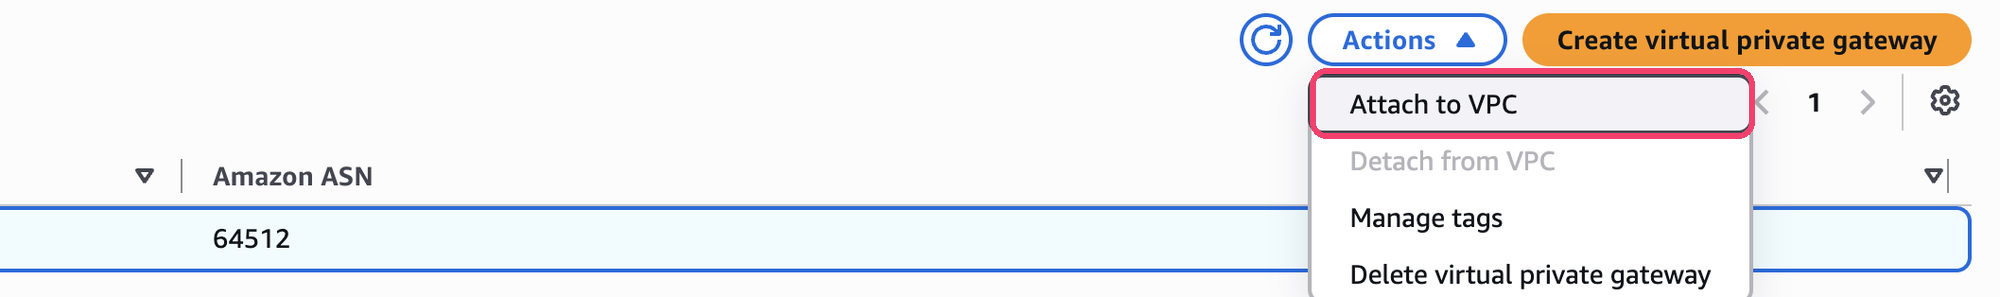
Select the gateway, click Actions → Attach to VPC, choose your VPC and click Attach to VPC.
Step 2: Create two customer gateways
Each customer gateway represents one Vipilink gateway.
- In the Vipilink console, open your network and note the public IP of each gateway.
-
In the AWS console, go to Virtual private network (VPN) → Customer gateways and click Create customer gateway.

-
Create the first customer gateway:
Field Value Name tag vipilink-gw-new-jerseyBGP ASN 64520IP address Public IP of the first Vipilink gateway 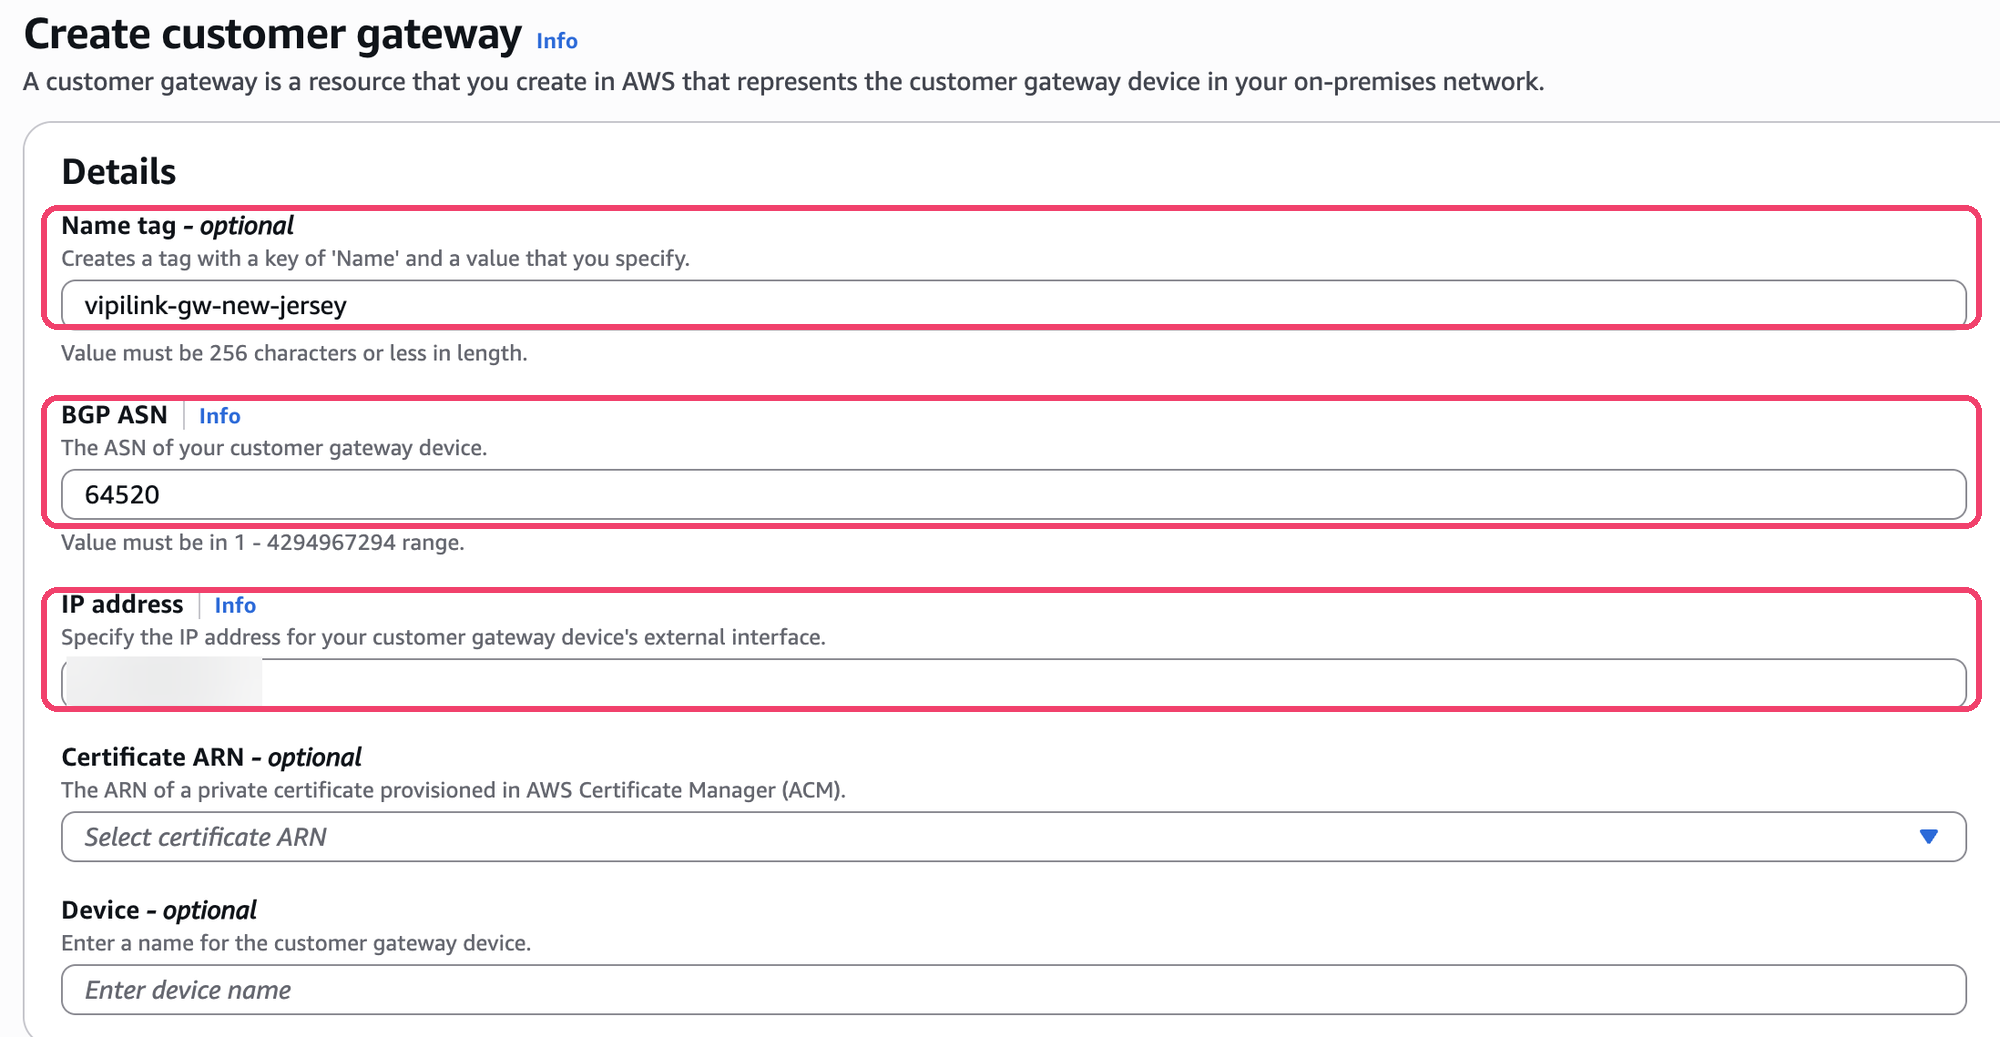
-
Repeat for the second gateway, for example
vipilink-gw-miami, with BGP ASN64520and the public IP of the second Vipilink gateway.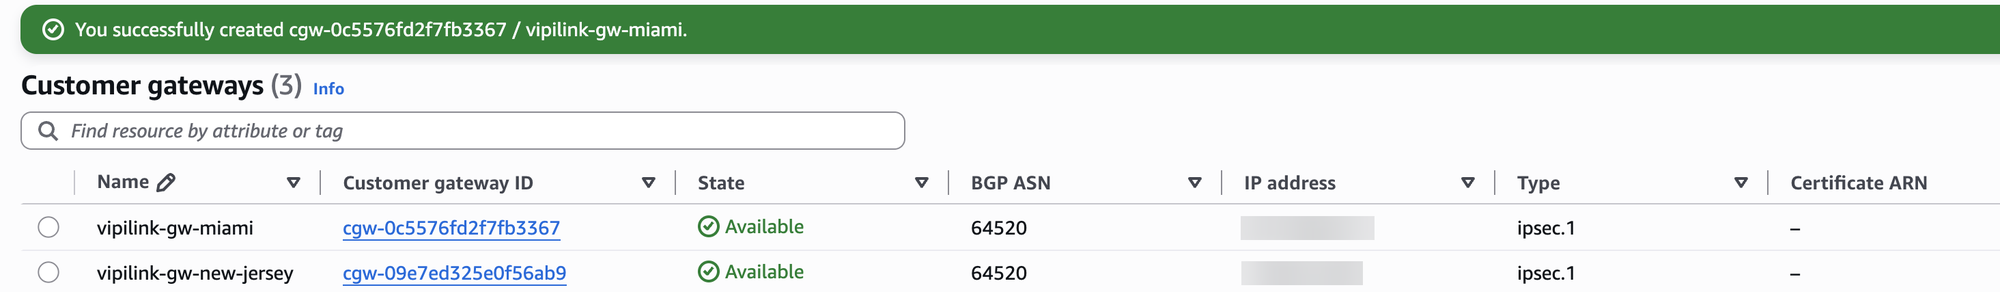
BGP ASN 64520
Vipilink gateways use ASN 64520. The customer gateways must use the same number, or BGP will not come up.
Step 3: Create two Site-to-Site VPN connections
Create one VPN connection for each customer gateway.
-
Go to Virtual private network (VPN) → Site-to-Site VPN connections and click Create VPN connection.

-
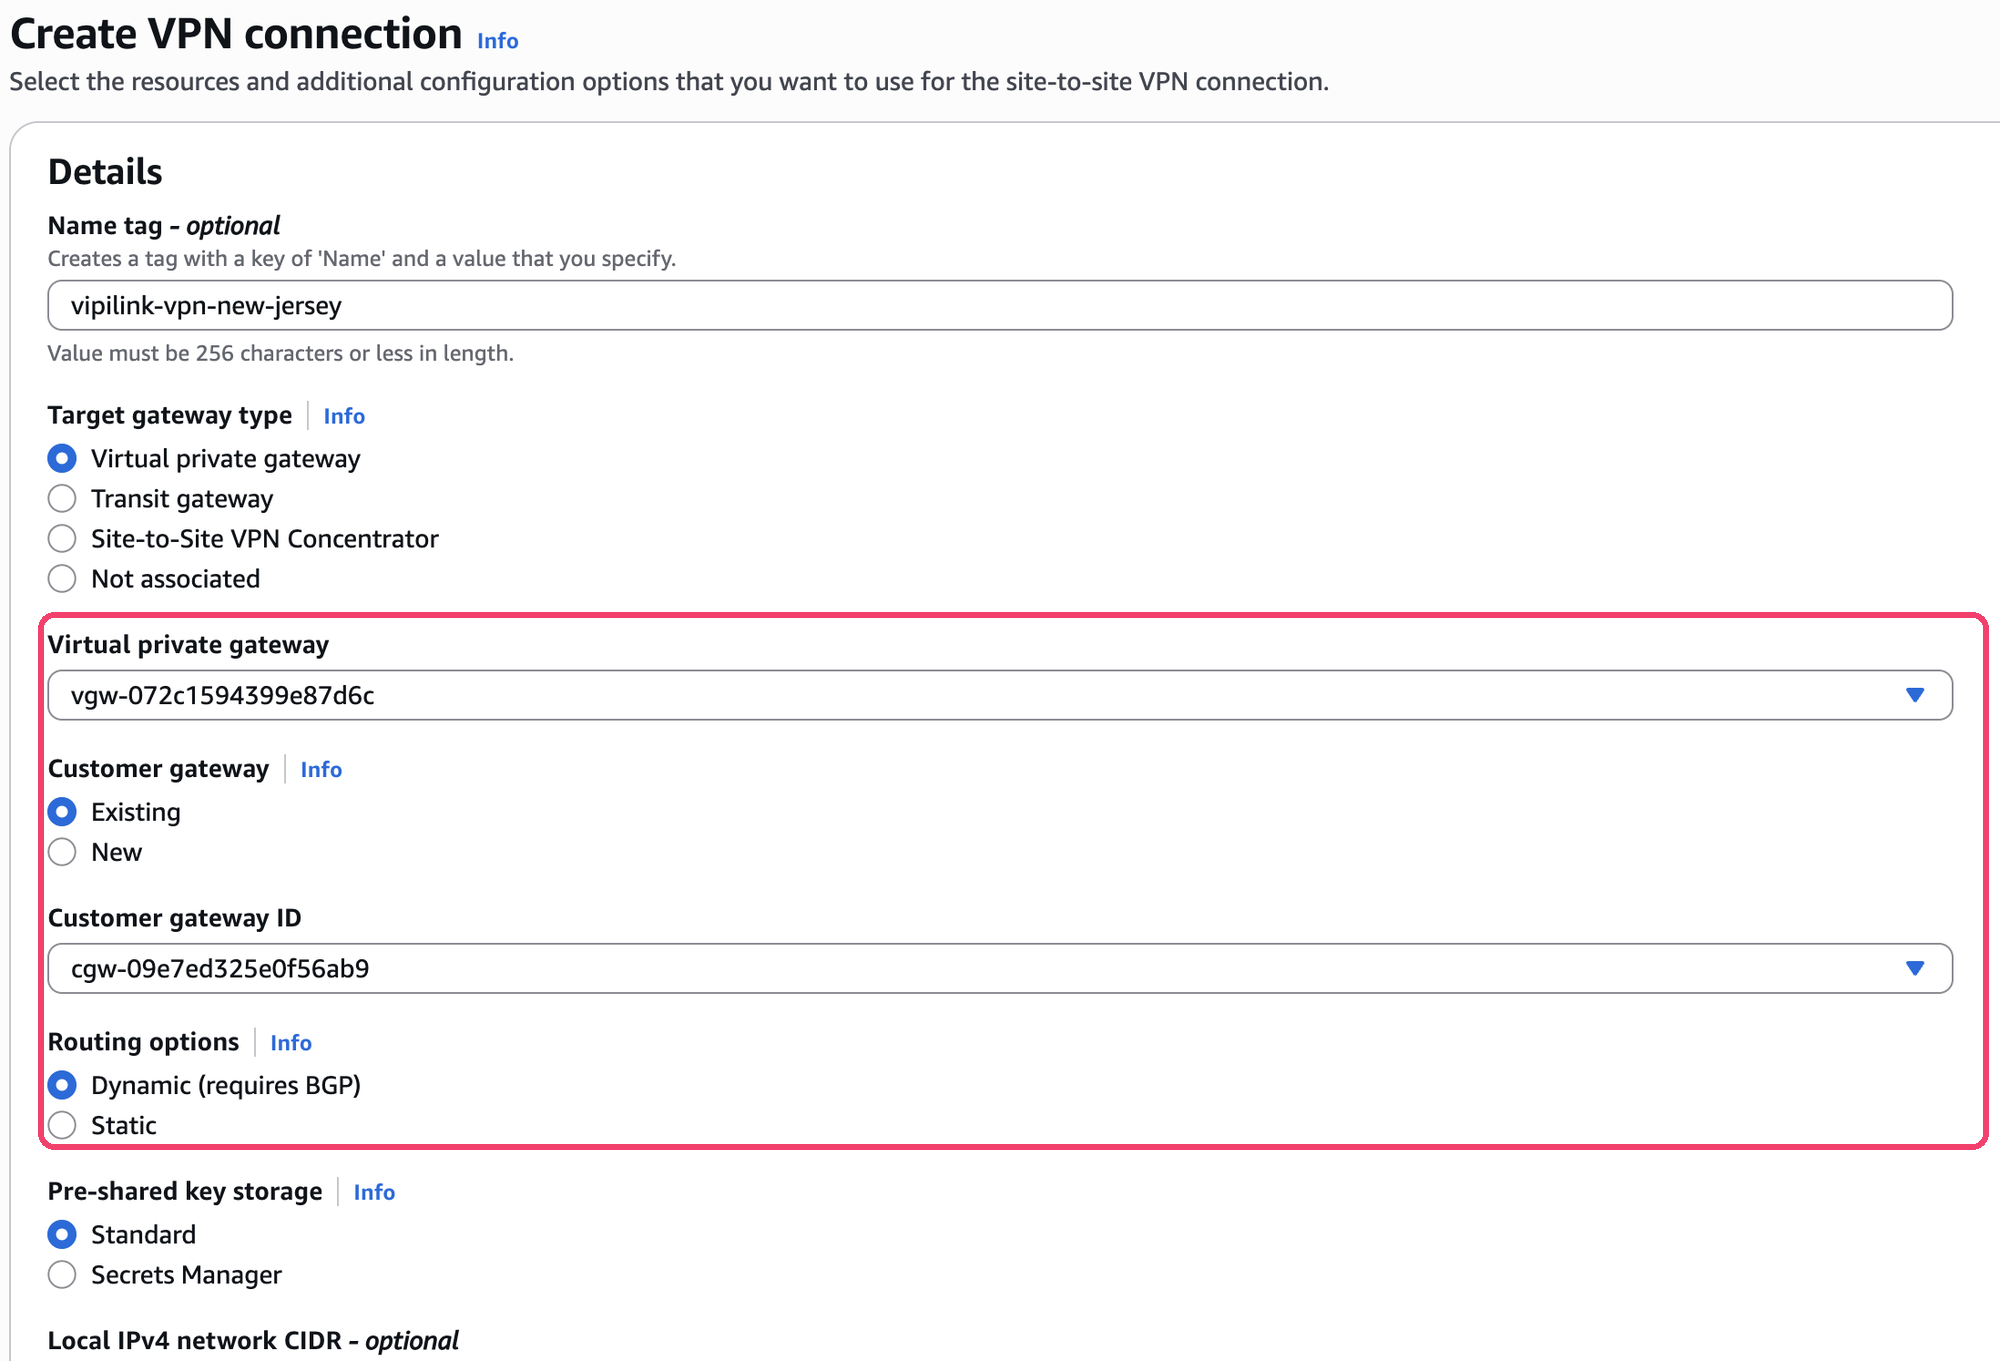
Fill in the form:
Field Value Name tag vipilink-vpn-new-jerseyTarget gateway type Virtual private gateway Virtual private gateway vipilink-vgwCustomer gateway Existing, then choose vipilink-gw-new-jerseyRouting options Dynamic (requires BGP) Leave the other fields at their defaults.
-
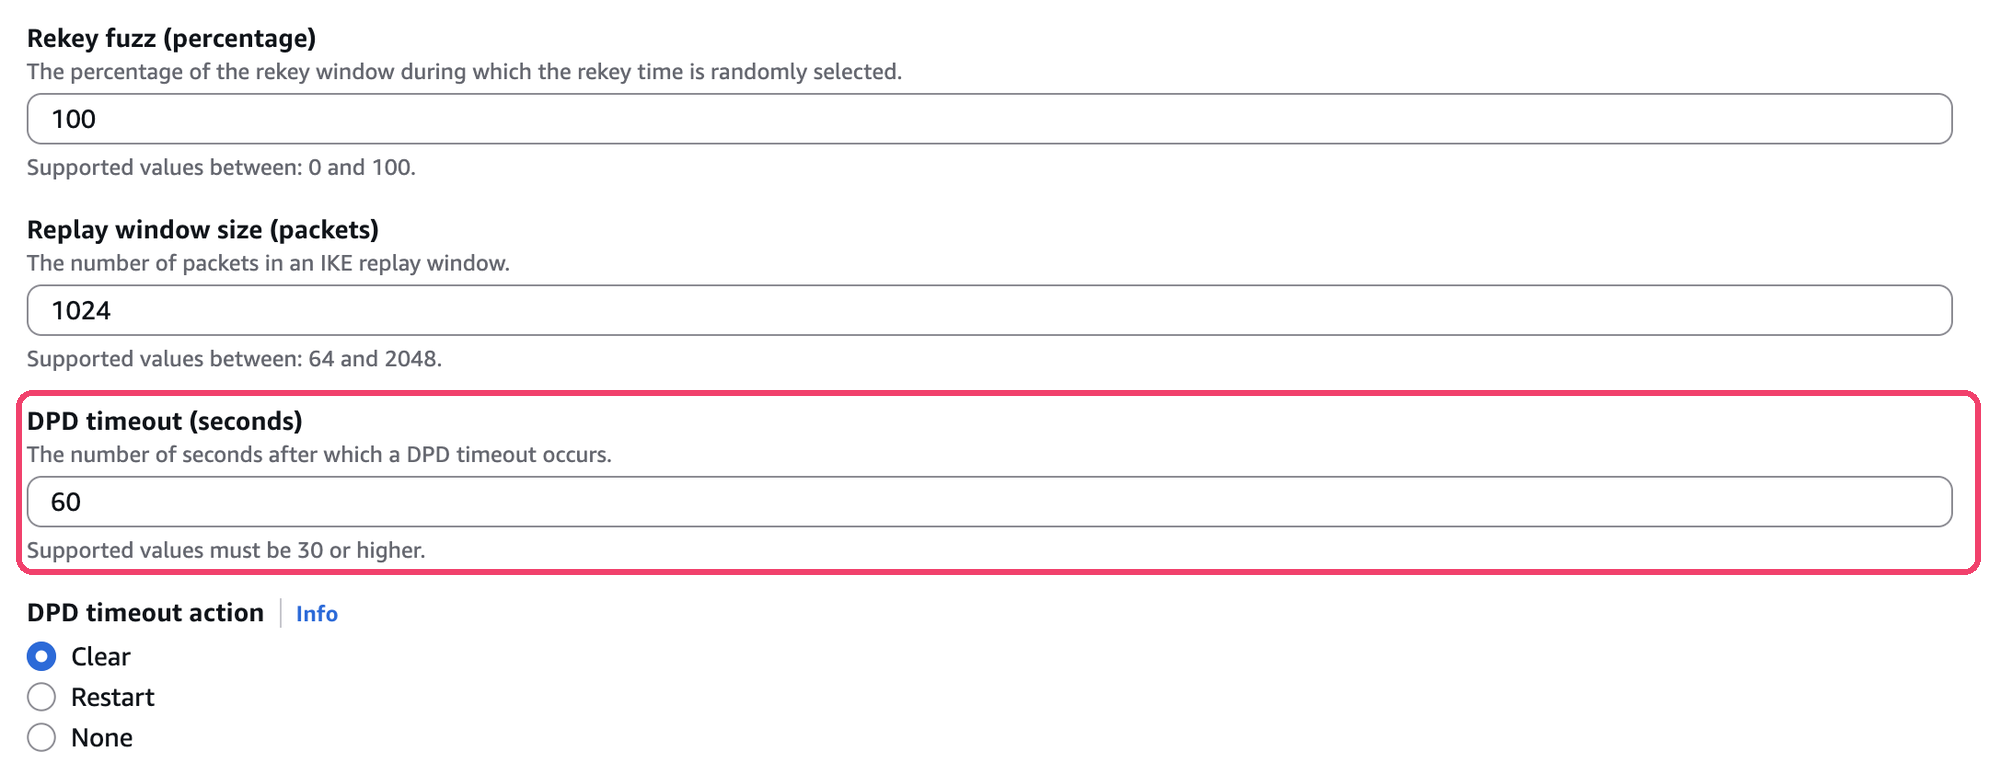
Expand Tunnel 1 options, choose Edit tunnel 1 options and set DPD timeout (seconds) to
60.
-
Click Create VPN connection.
- Repeat for the second customer gateway, for example
vipilink-vpn-miami.
Wait until both connections show Available.

Step 4: Download both configuration files
-
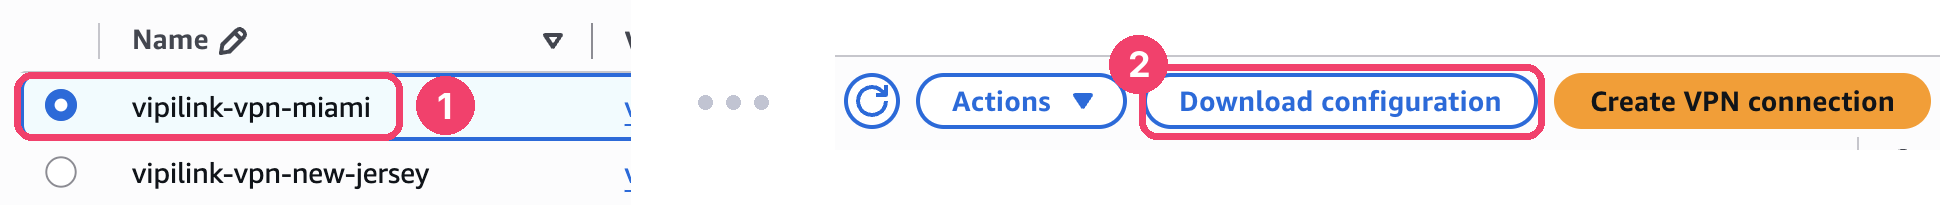
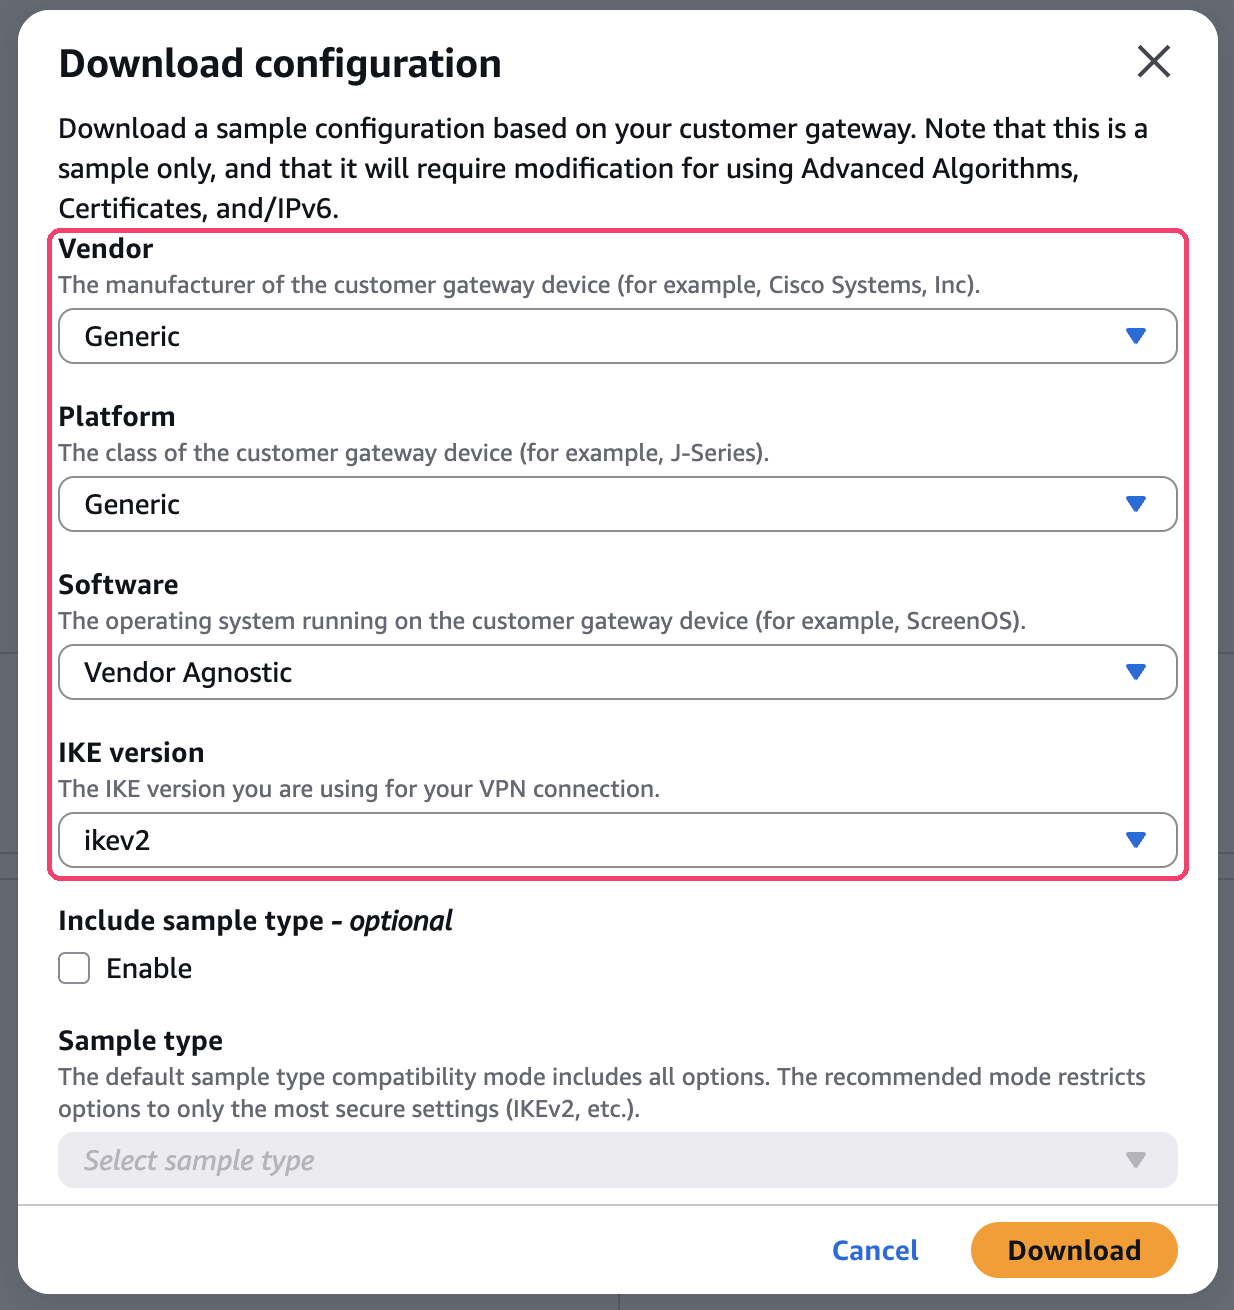
Select the first VPN connection (1) and click Download configuration (2).
-
Choose Generic, Generic, Vendor Agnostic and ikev2, then click Download.
-
Repeat for the second VPN connection. Rename the files so you know which gateway each one belongs to, for example add
-new-jerseyand-miamito the names.
Keep the files private
The configuration files contain the tunnel pre-shared keys. Store them somewhere safe and delete them when you are done.
Step 5: Route VPC traffic to Vipilink
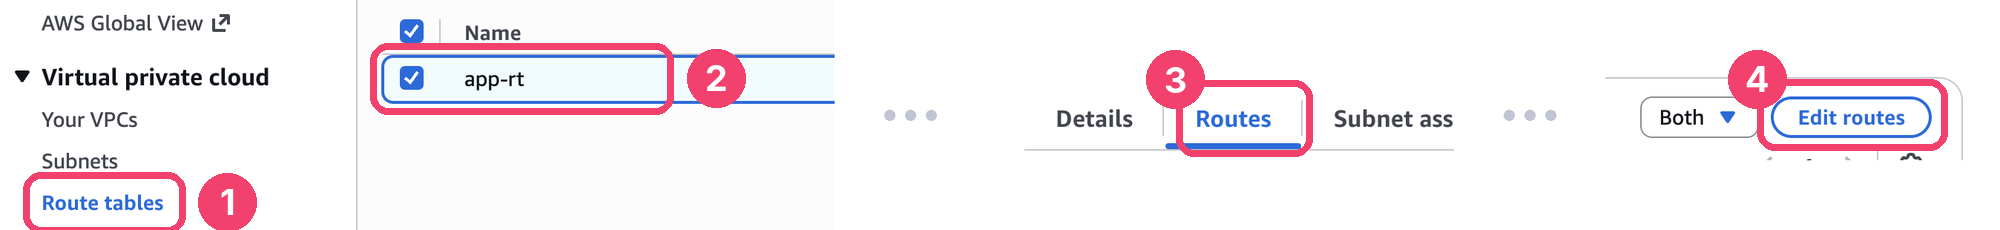
- Go to Virtual private cloud → Route tables (1) and select the route table used by your VPC subnets (2).
-
Open the Routes tab (3) and click Edit routes (4).
-
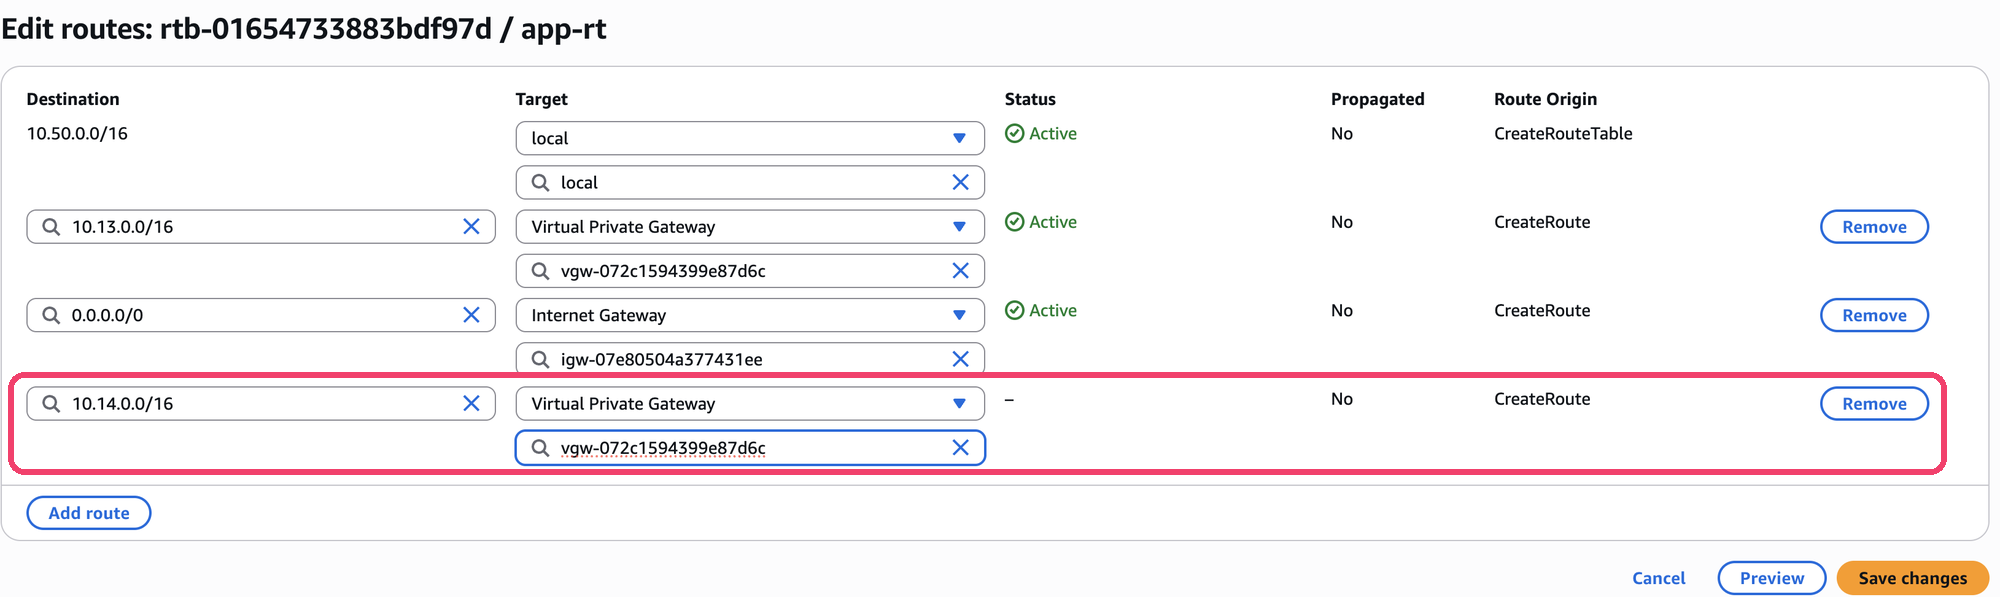
Click Add route:
- Destination: your Vipilink network subnet, for example
10.14.0.0/16 - Target: Virtual Private Gateway, then choose
vipilink-vgw
- Destination: your Vipilink network subnet, for example
- Click Save changes.
Step 6: Add the dual tunnel in Vipilink
-
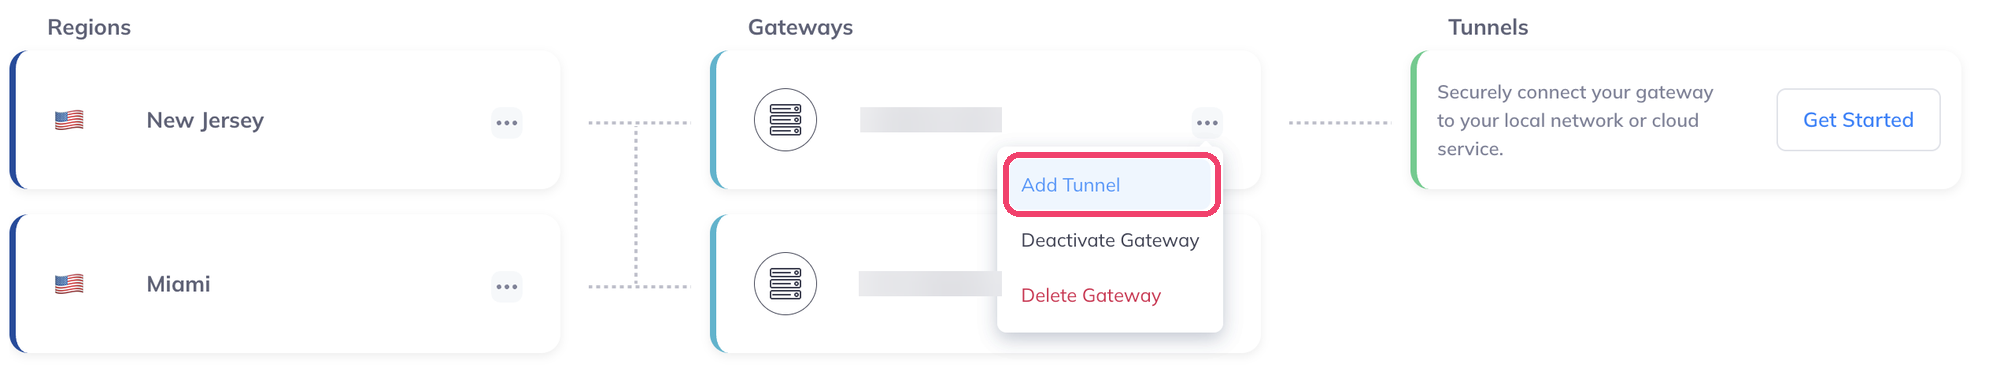
In the Vipilink console, open your network. On either gateway card, click the ... menu and choose Add Tunnel.
-
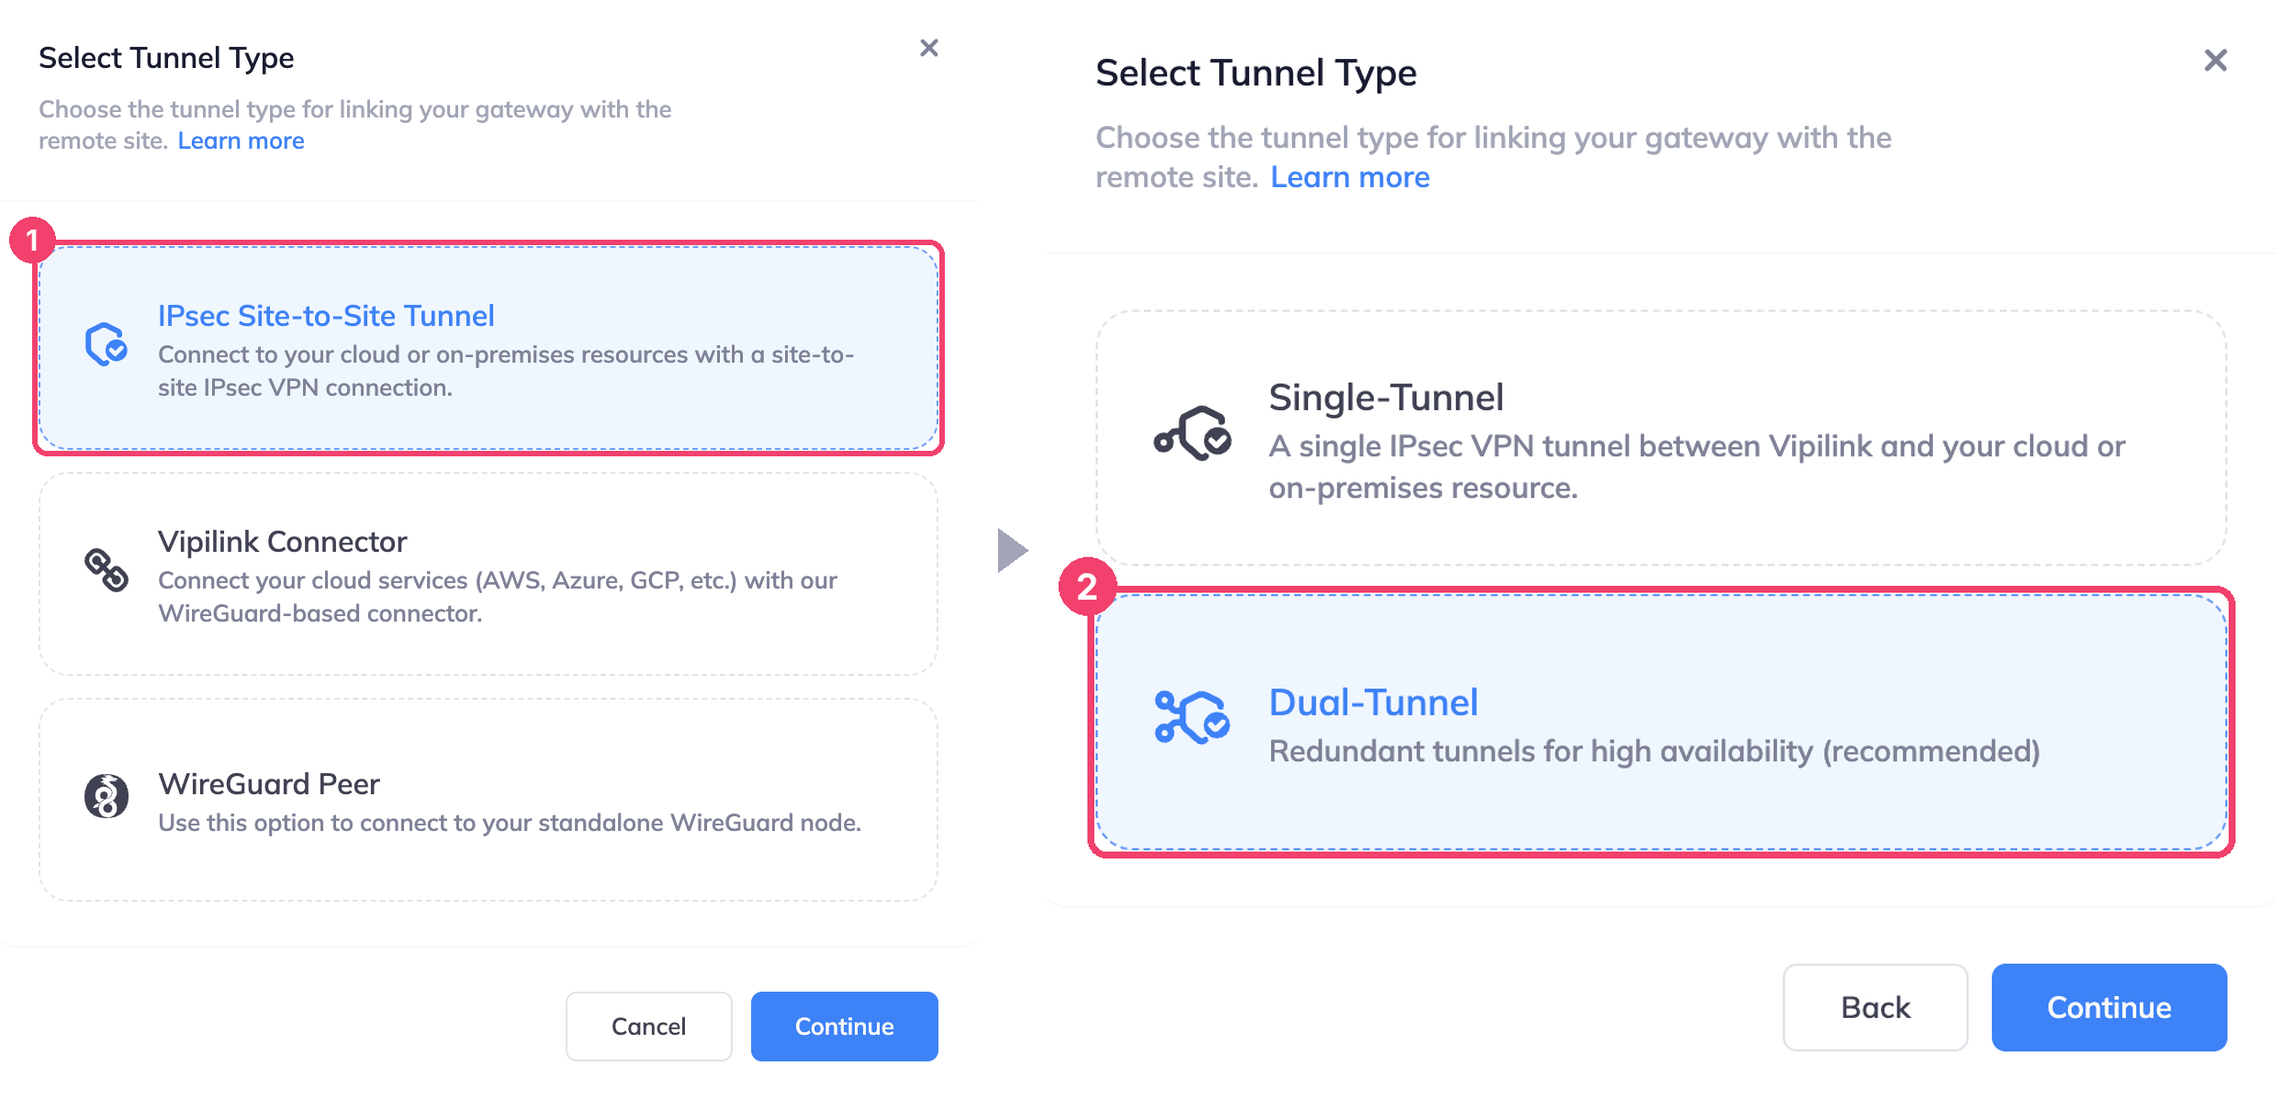
Choose IPsec Site-to-Site Tunnel (1) and click Continue. Then choose Dual-Tunnel (2) and click Continue.
Tip
Dual-Tunnel is only available when the network has at least two gateways.
-
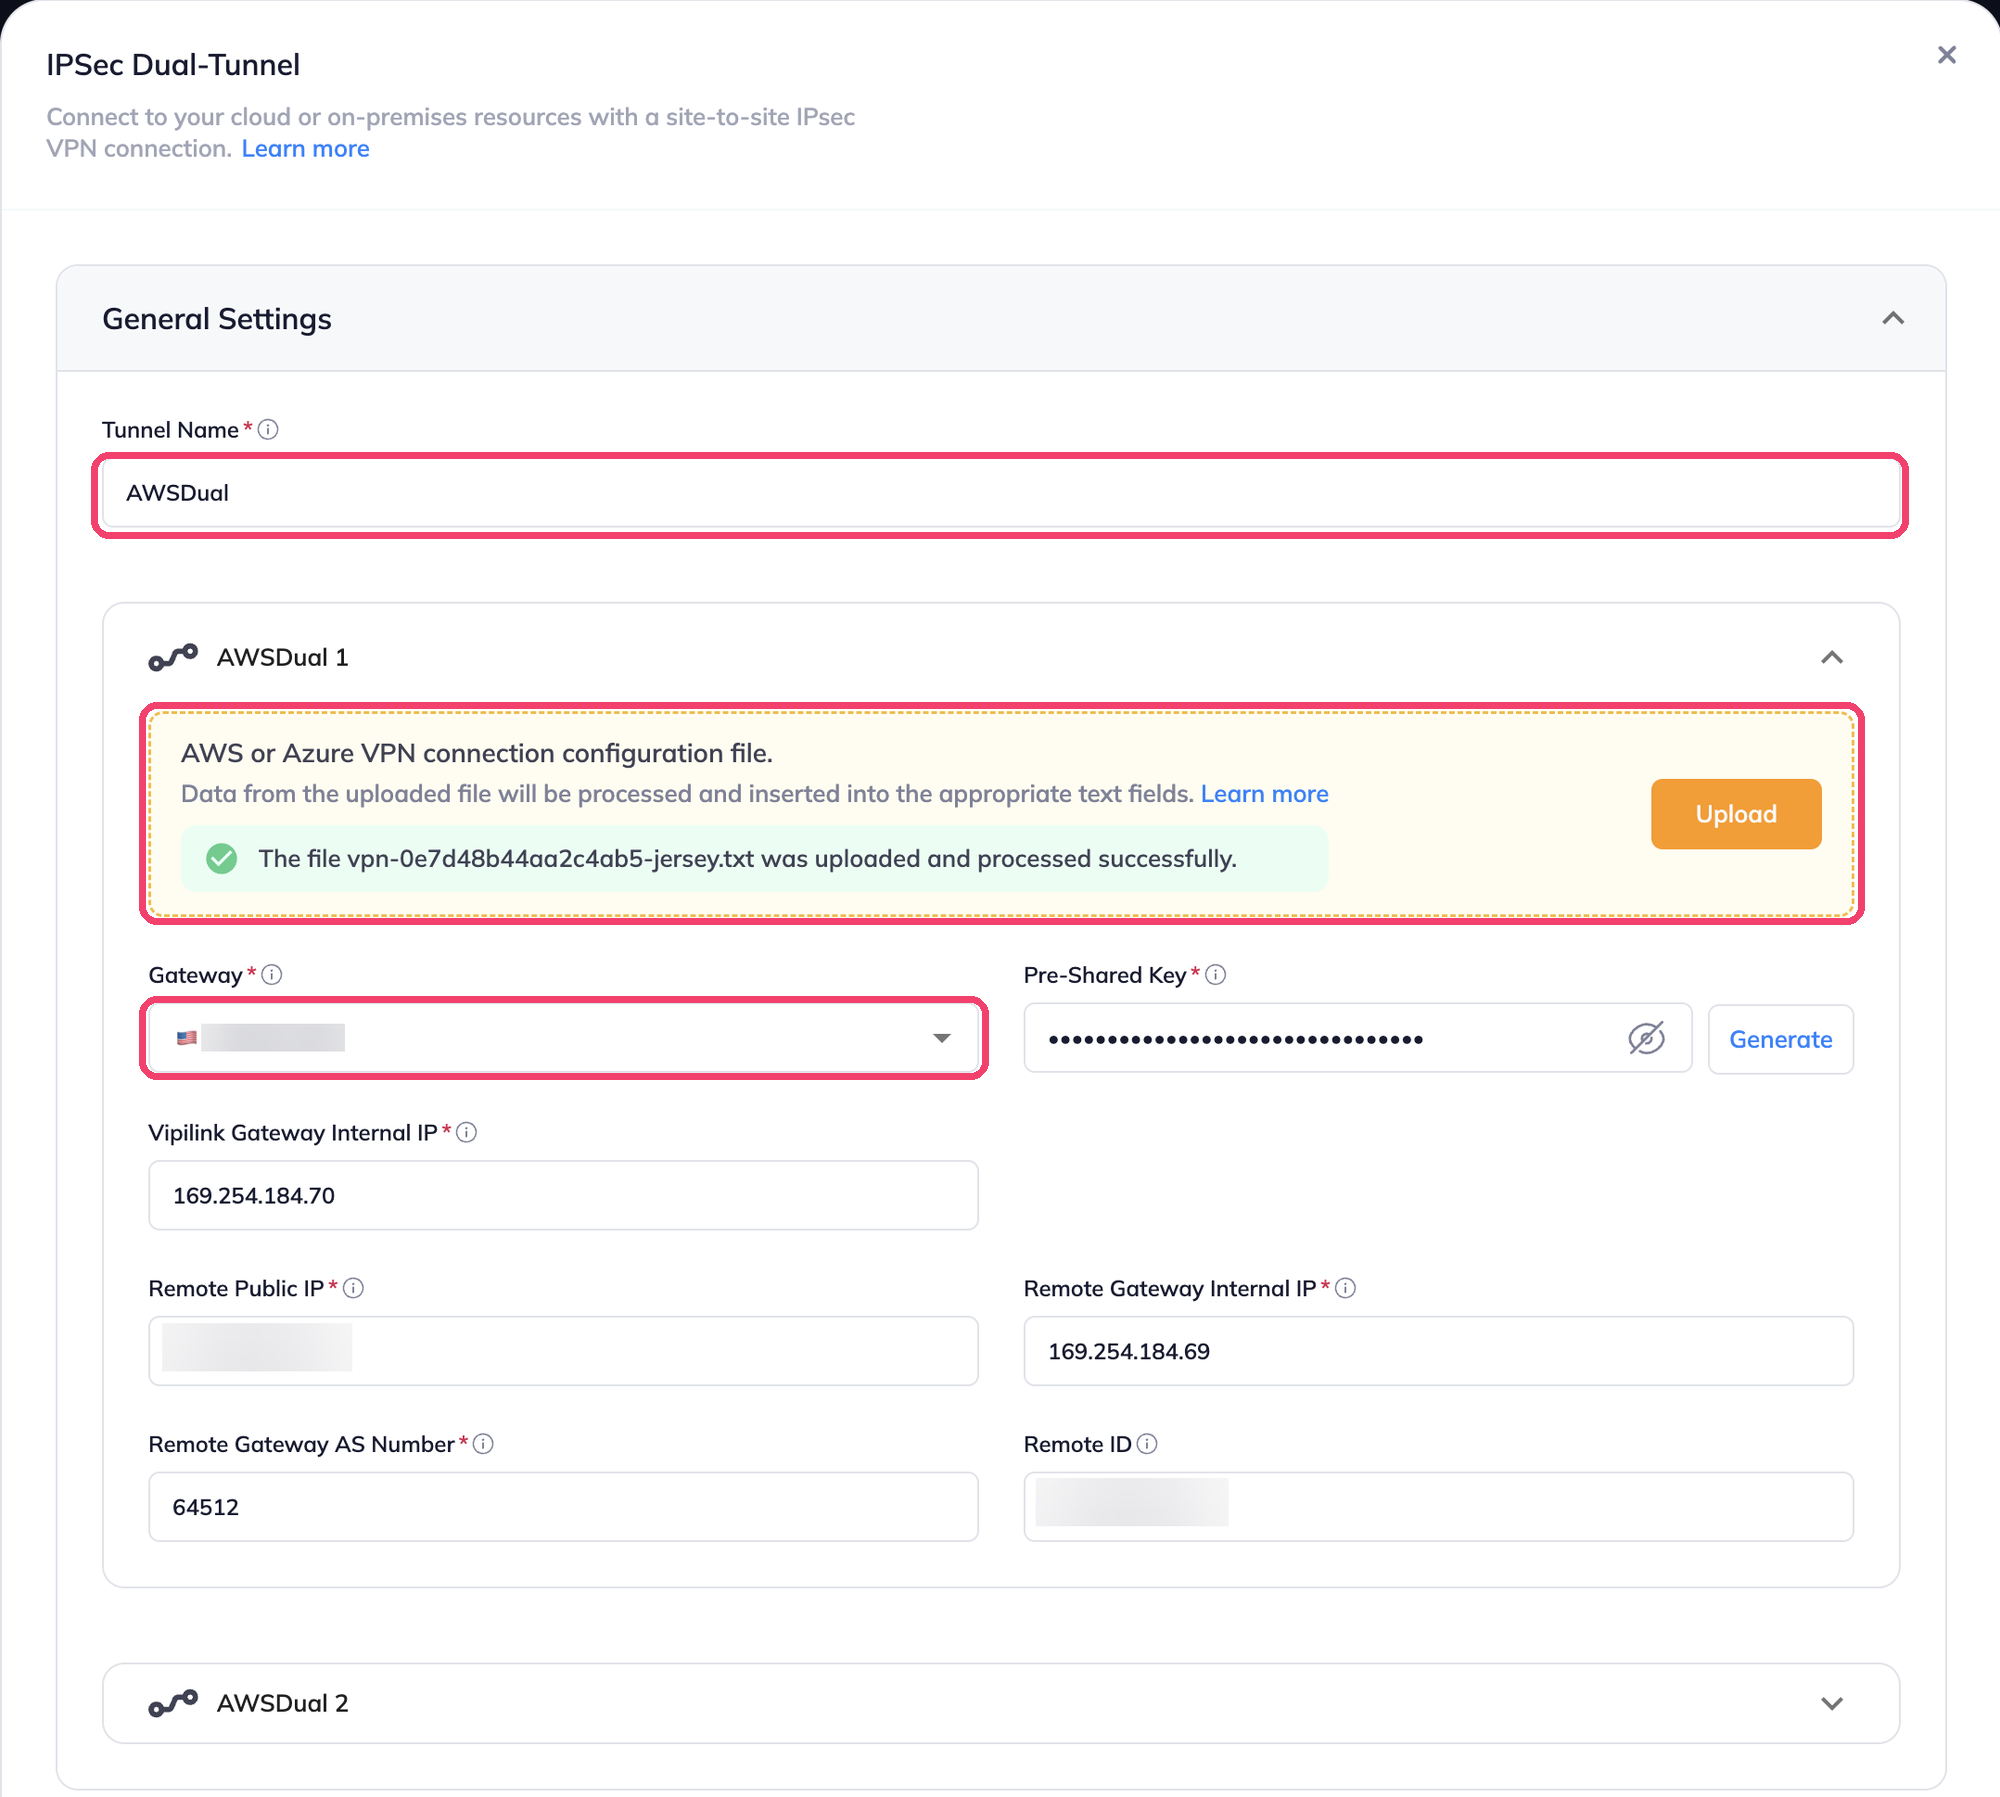
Enter a Tunnel Name, for example
AWSDual. Use letters and numbers only. Vipilink names the two tunnelsAWSDual 1andAWSDual 2. -
In the first tunnel section, click Upload and select the first configuration file. Then choose the matching Vipilink gateway in Gateway.
-
In the second tunnel section, upload the second file and choose the second Vipilink gateway.
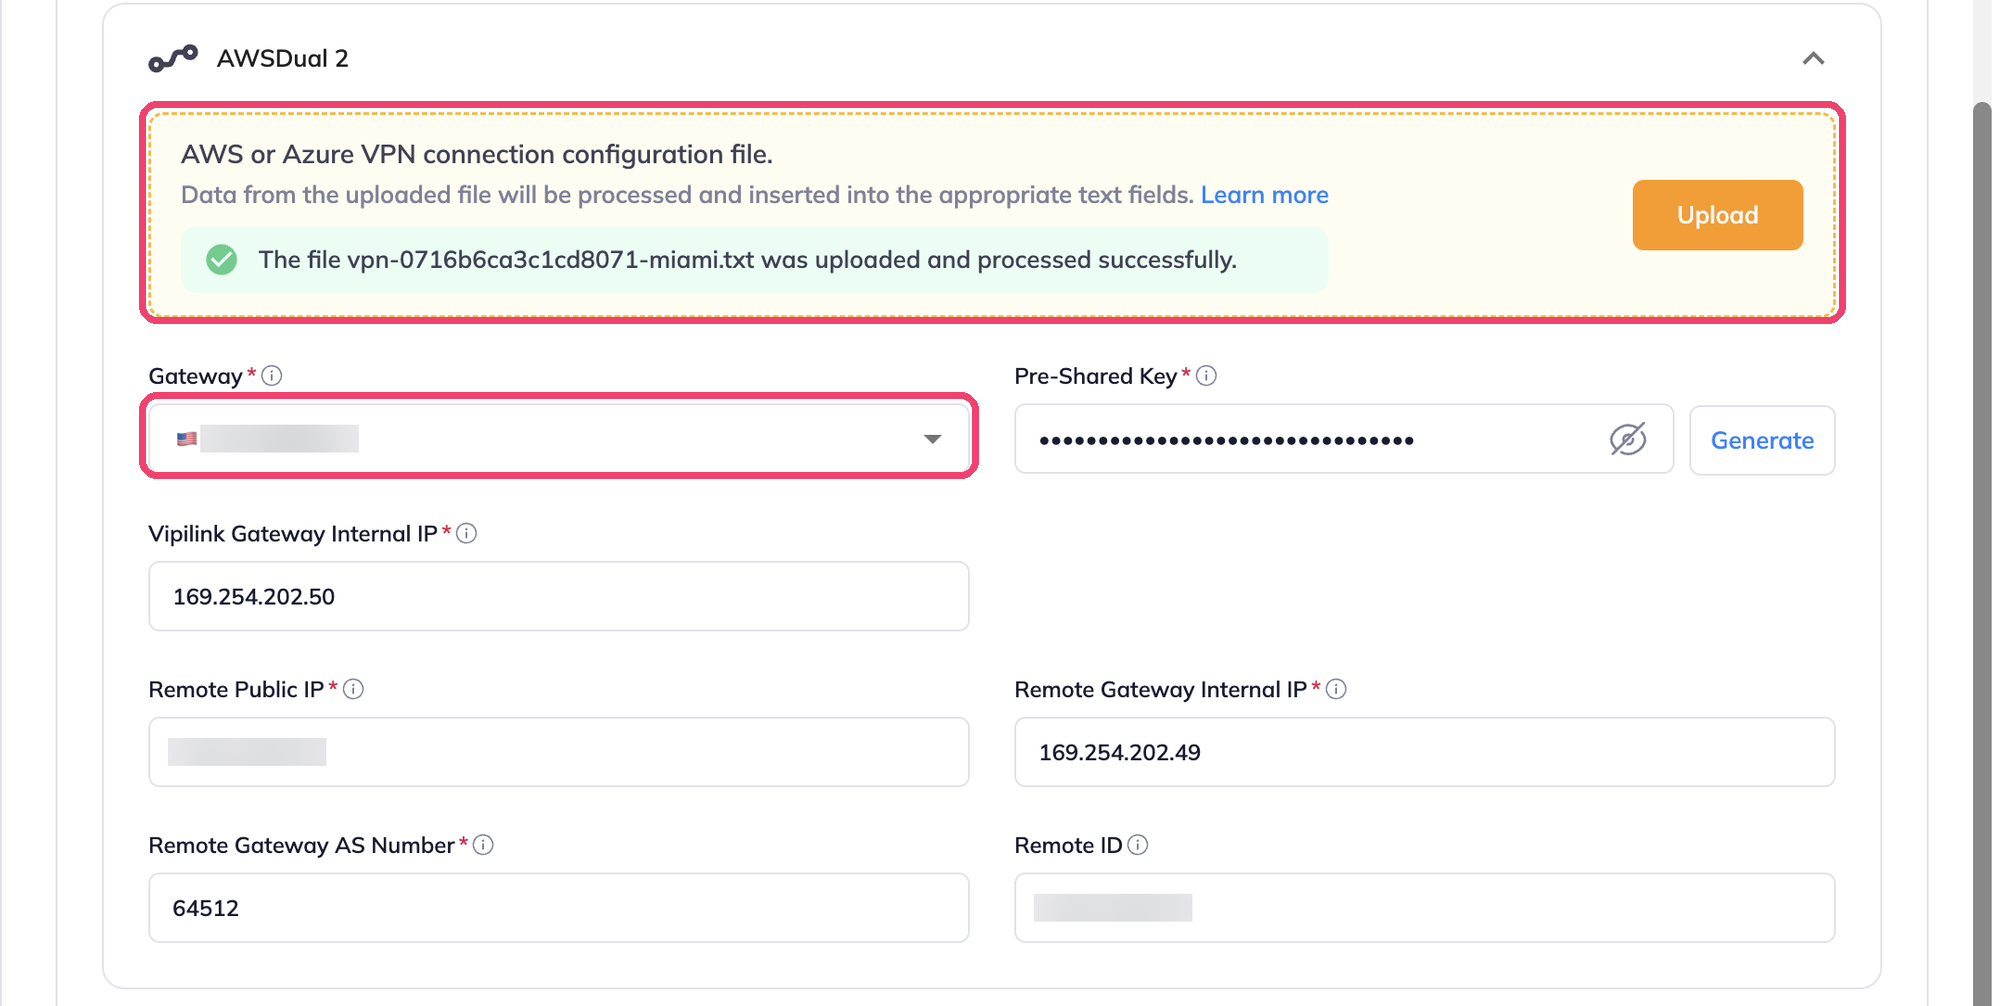
Vipilink fills in the pre-shared key, internal IPs, remote public IP, remote AS number and remote ID from each file.
Match each file to its gateway
Each file belongs to the customer gateway you created for one Vipilink gateway. If you pick the wrong gateway for a file, that tunnel will not come up.
-
In Shared Settings, keep Vipilink Side Subnets and Remote Side Subnets set to Any. The Vipilink ASN is fixed at
64520.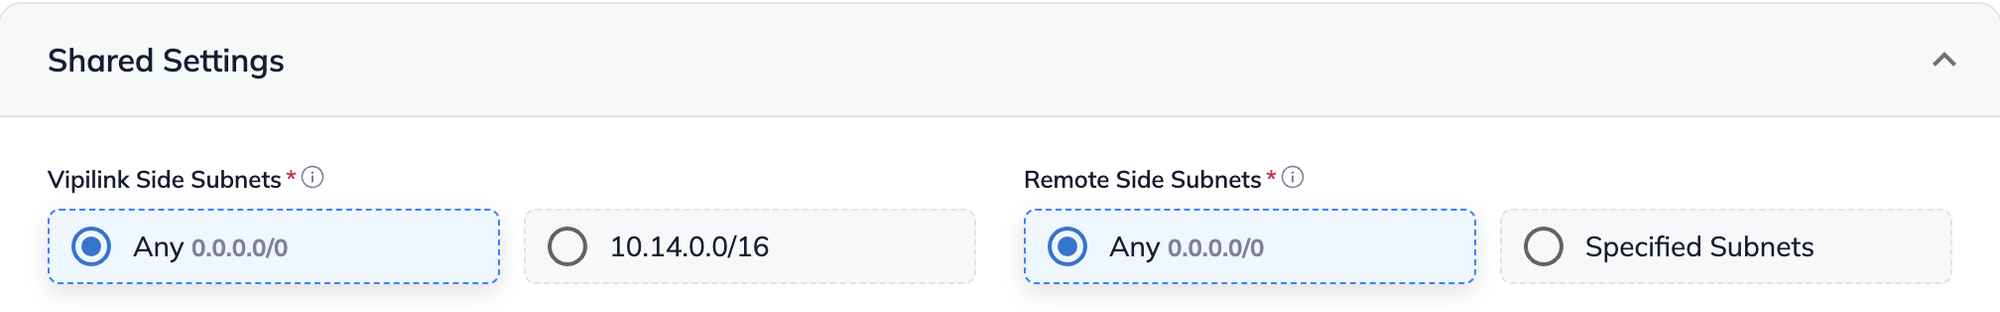
-
Keep the Advanced Settings defaults: IKE V2, IKE lifetime 8h, tunnel lifetime 1h, DPD 10s / 30s, aes256, sha256 and group 14.
- Click Add Tunnel.
Step 7: Route Vipilink traffic to the VPC
-
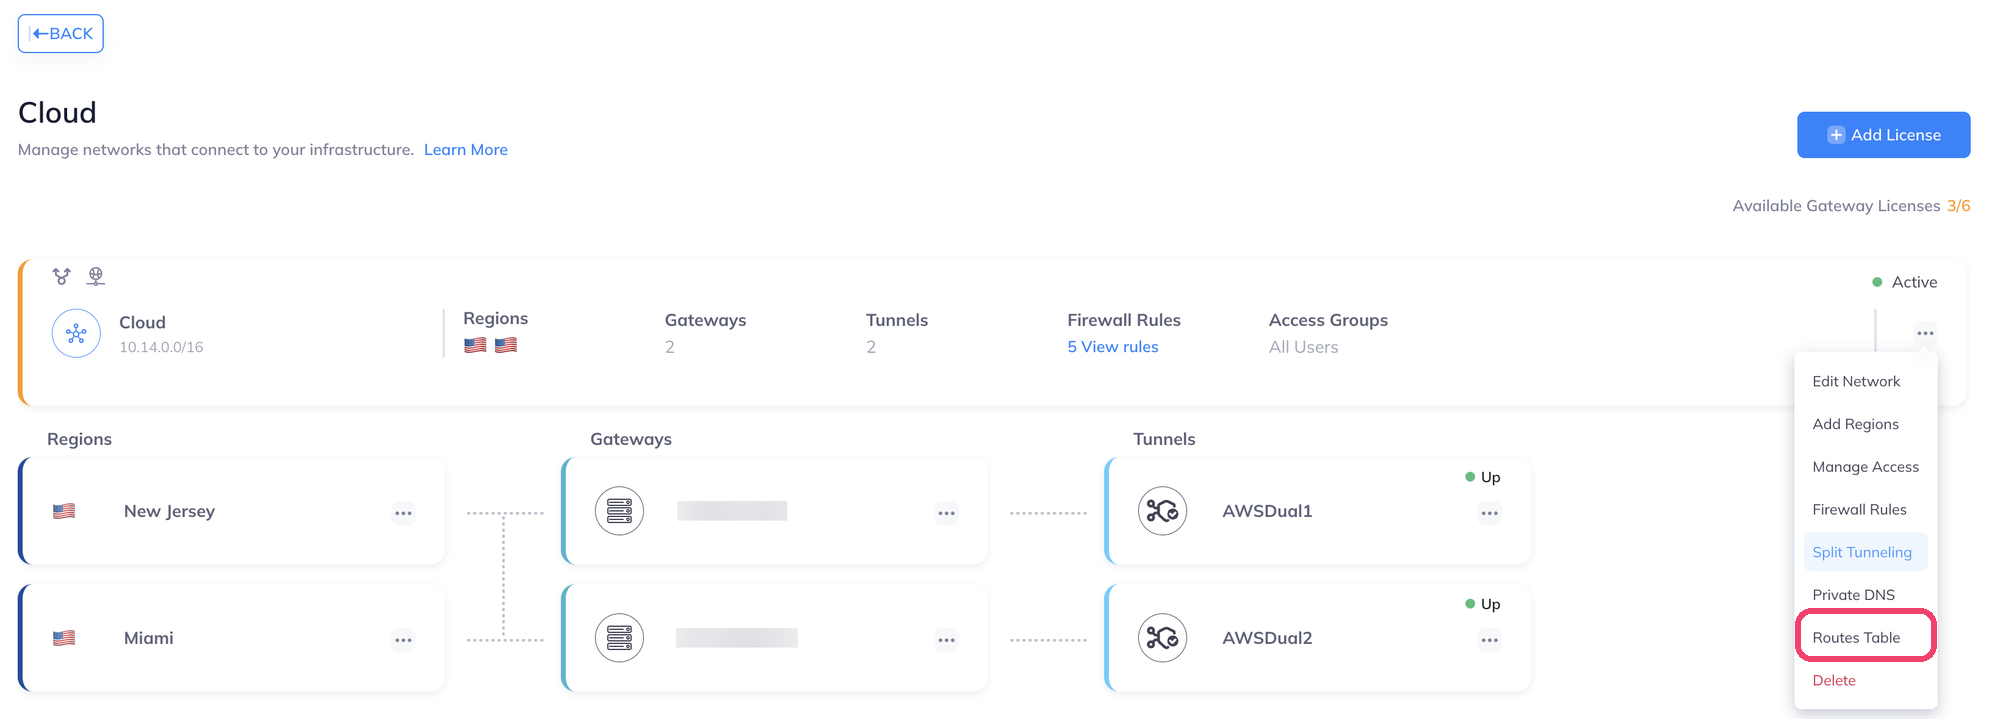
On the network card, click the ... menu and choose Route Table.
-
Click Add Routes, choose the dual tunnel, enter the VPC CIDR (for example
10.50.0.0/16) and click Add Routes.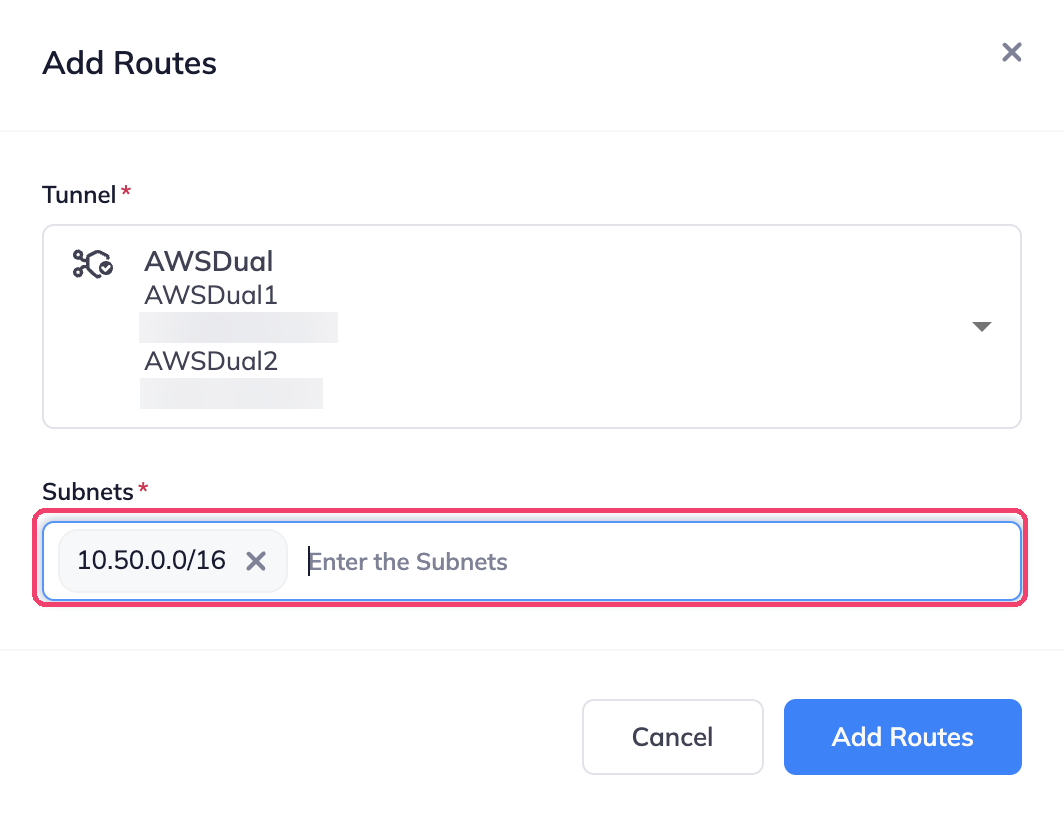
-
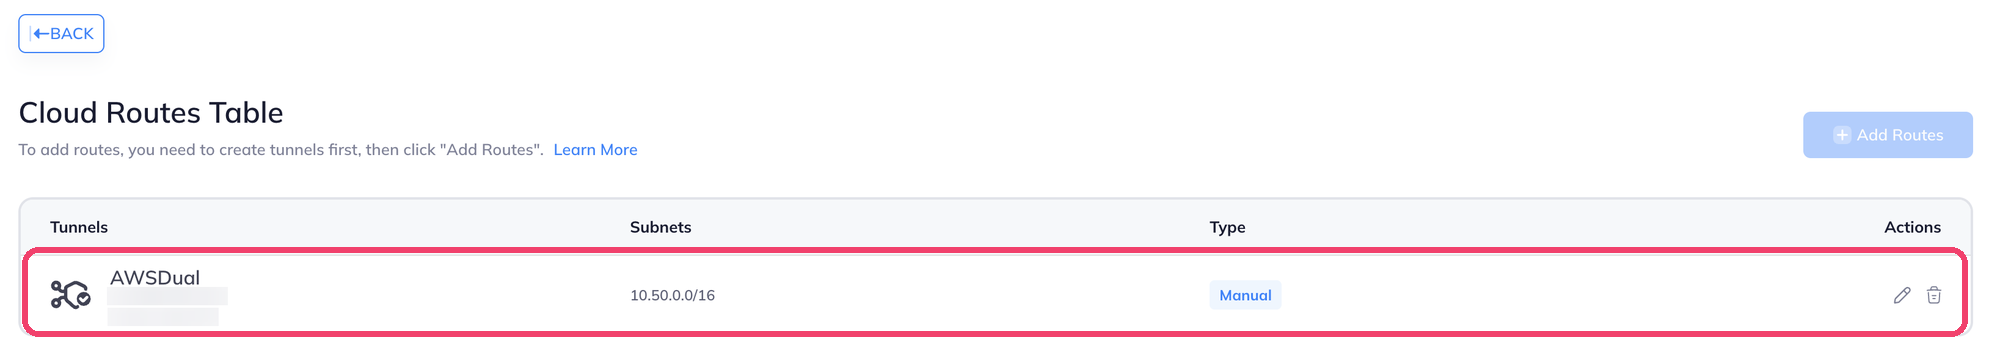
The route appears in the table with the type Manual. It covers both tunnels.
Step 8: Check the connection
-
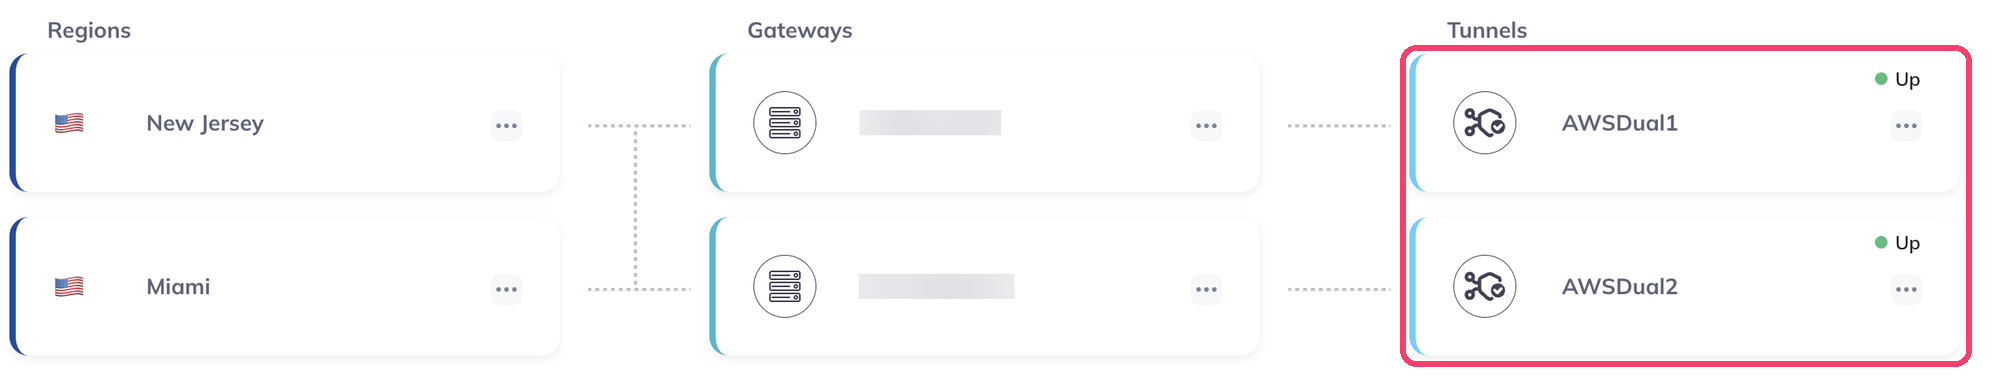
In the Vipilink console, both tunnel cards show Up.
-
In the AWS console, open Tunnel details for each VPN connection. One tunnel shows Up with BGP routes in Details.

One tunnel per VPN connection shows Down
This is expected. AWS creates two tunnels for every VPN connection, and each Vipilink gateway uses one of them. AWS also shows a banner saying the connection is not using both tunnels. Redundancy comes from the two VPN connections and the two Vipilink gateways.
-
Connect a device to the network with the Vipilink agent and reach a resource in the VPC, for example with
pingor SSH to a private IP.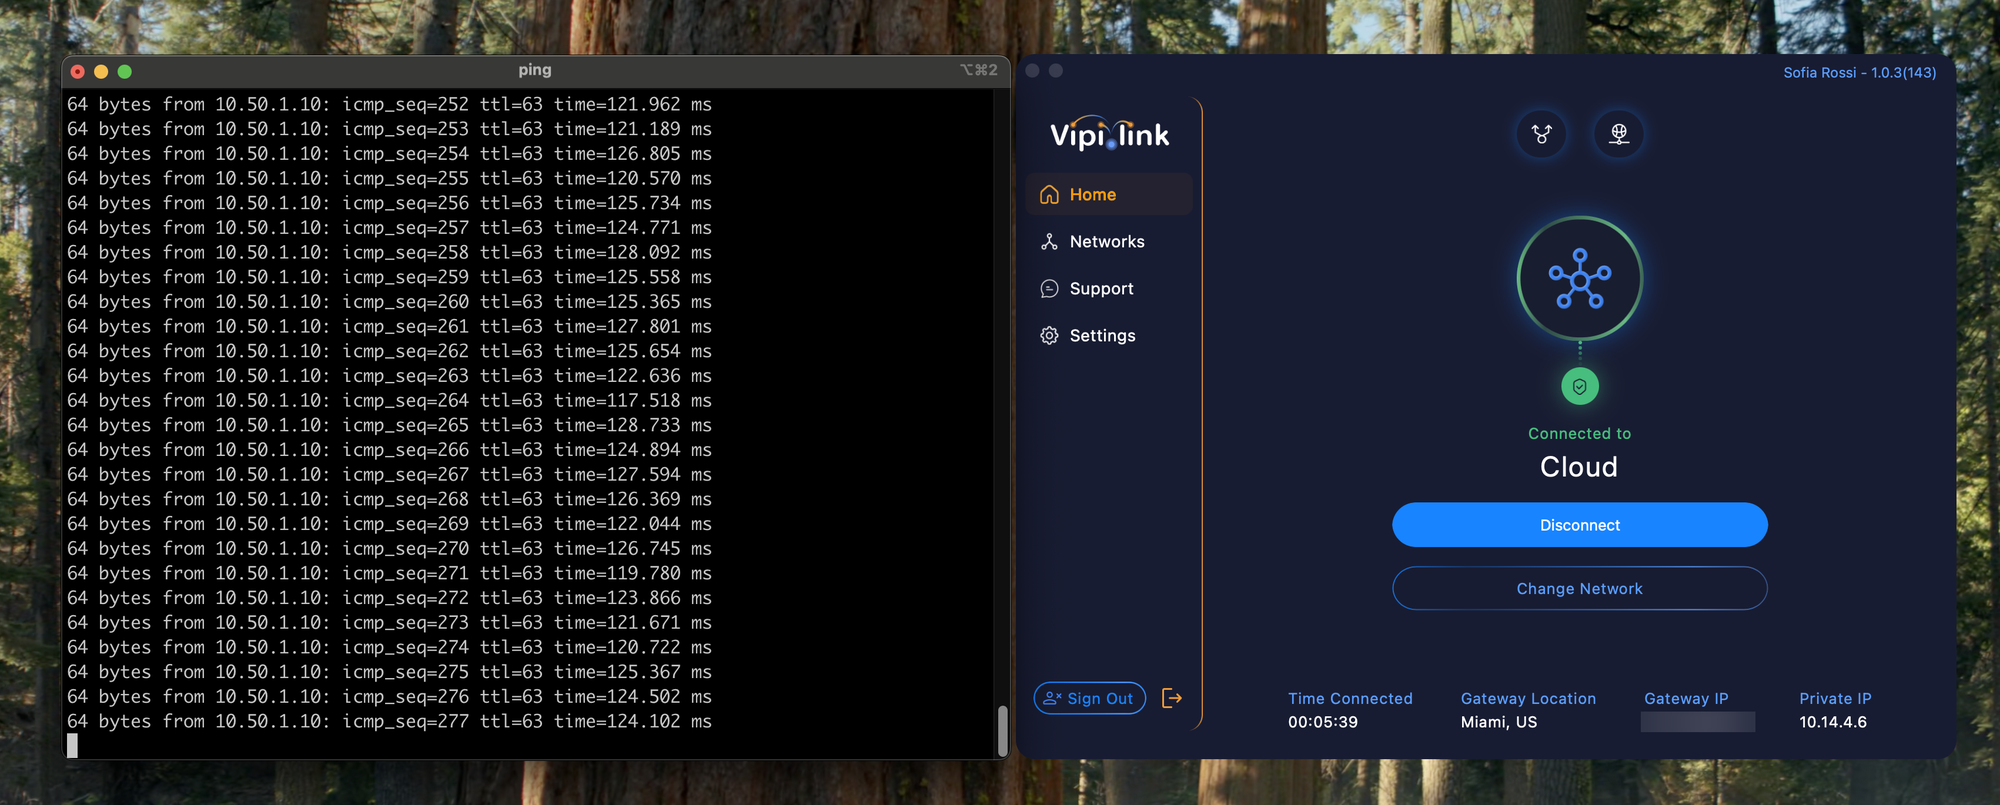
Troubleshooting
| Problem | What to check |
|---|---|
| A tunnel stays Down | The customer gateway IP matches that Vipilink gateway's public IP. The file uploaded in that section belongs to that gateway's VPN connection. The customer gateway BGP ASN is 64520. |
| Tunnels are Up but nothing responds | Routes exist on both sides (Step 5 and Step 7). Security groups and network ACLs in AWS allow traffic from the Vipilink network subnet. Vipilink firewall rules allow the traffic. |