IPsec site-to-site VPN with SonicWall
1. Log in to the Vipilink portal and create a network
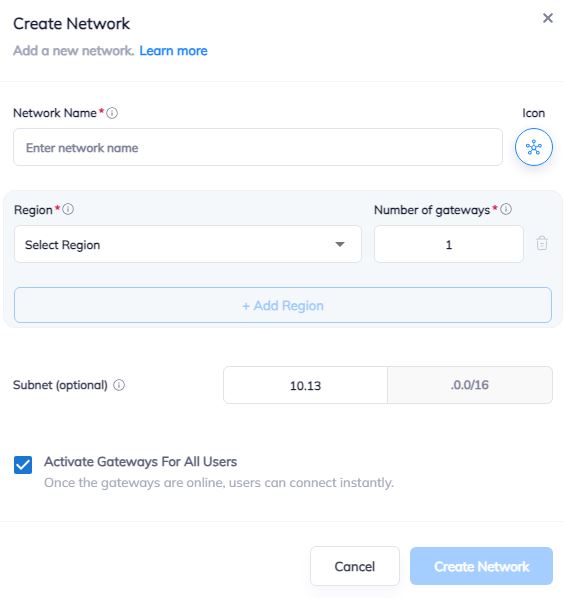
1.1 Go to Networks section and create a new network.
1.2 Define the network name.
1.3 Select the region and gateways number.
1.4 Choose the subnet.
1.5 Activate gateways for all users section is active by default. If you want to disable this function - just remove the mark.
2. Create the IPsec tunnel in the Vipilink portal
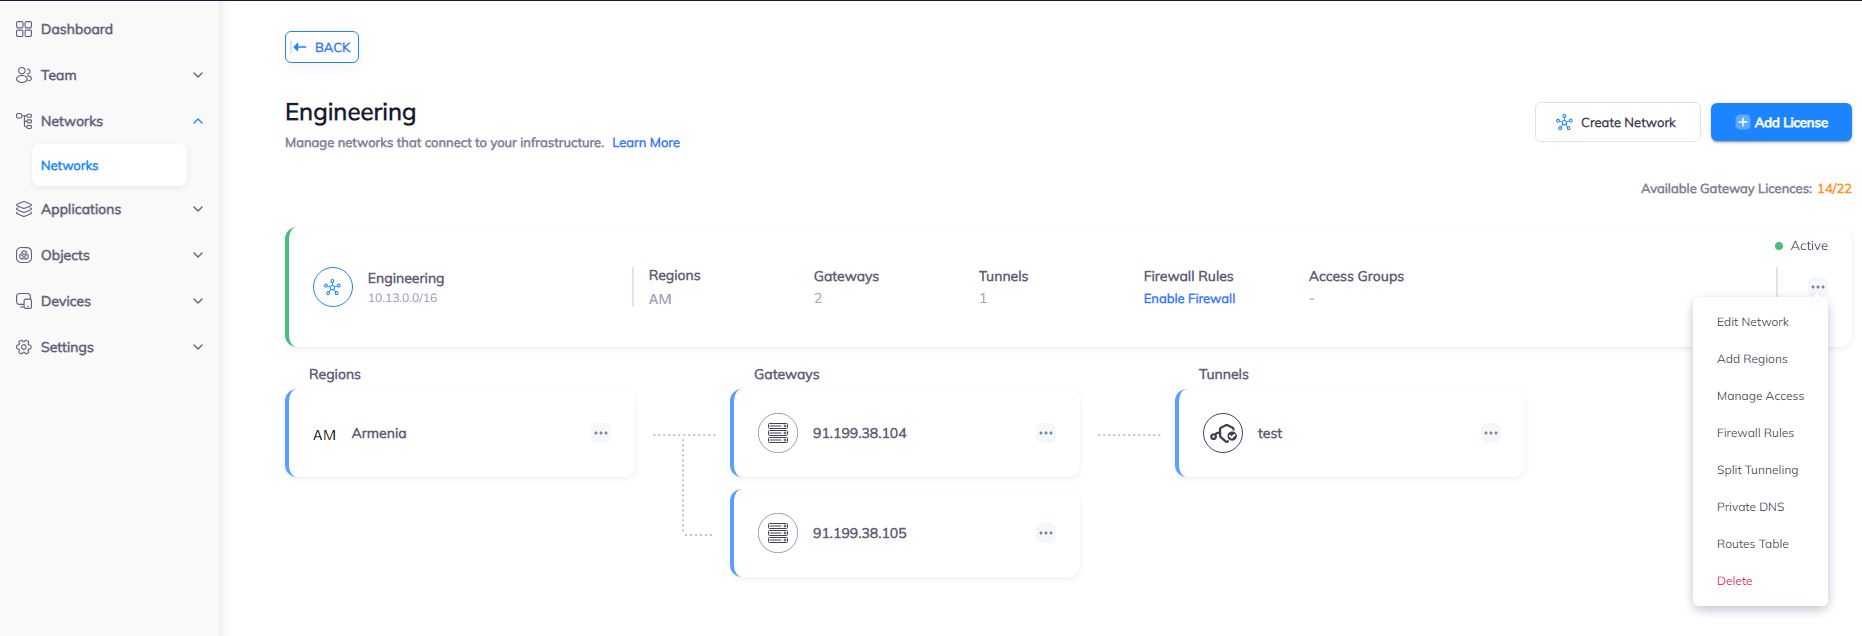
2.1 Go to Networks section and click on the subnet that you created in Step-1.
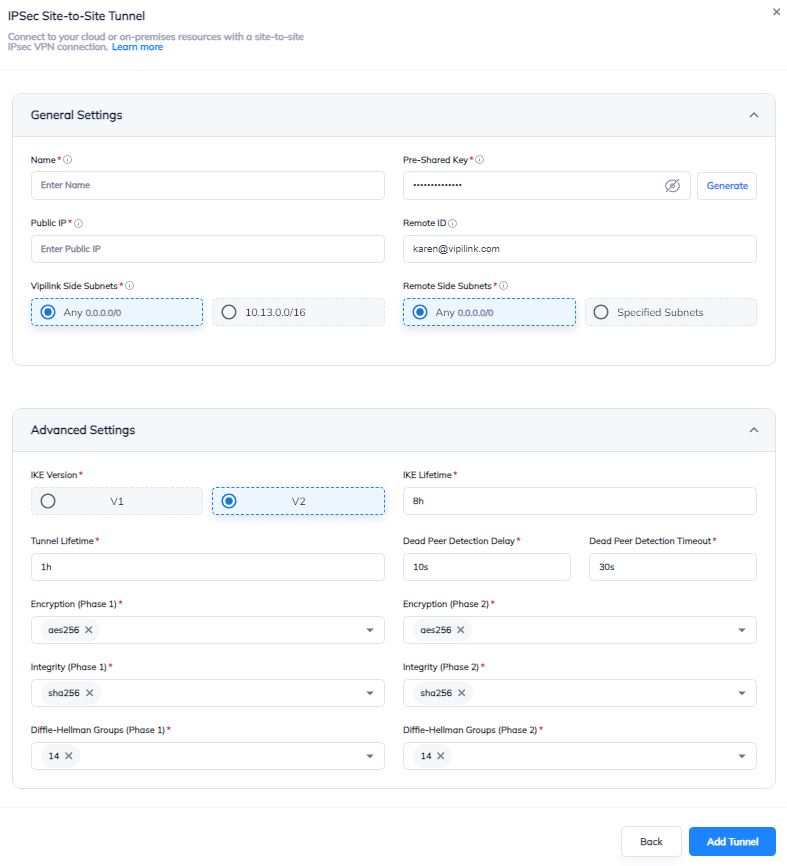
2.2 Click on Gateway and add a Tunnel. Choose IPSec Site-to-Site Tunnel and press to continue.
2.3 Choose between a Single-Tunnel and Dual-Tunnel.
2.4 General Settings Values
-
Name
-
Public IP
-
Vipilink Side Subnets
-
Pre-Shared Key
-
Remote ID
-
Remote Side Subnets
2.5 Advanced Settings Values
-
Ike Version
-
Tunnel Lifetime
-
Encryption (Phase 1)
-
Integrity (Phase 1)
-
Diffie-Helman Groups (Phase 1)
-
Ike Lifetime
-
Dead Peer Detection Delay
-
Dead Peer Detection Timeout
-
Encryption (Phase 2)
-
Integrity (Phase 2)
-
Diffie-Helman Groups (Phase 2)
2.6 You can also manage a Network, Regions, Access, Firewall Rules, Route Table, enable Split Tunneling and Private DNS.
3. Create the IPsec tunnel on Sonicwall
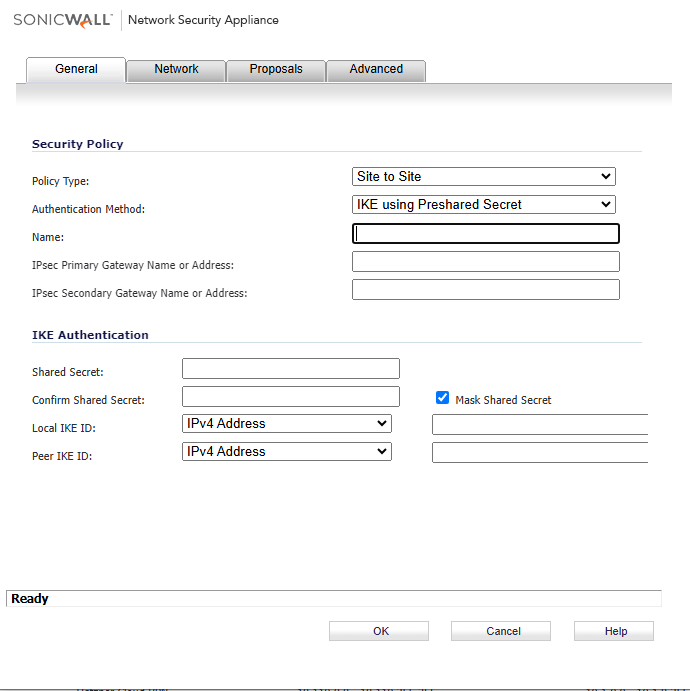
3.1 Log in to Sonicwall Web Interface and navigate to VPN/Settings. Click to add in VPN Policies section.
3.2 General Values
-
Policy Type
-
Authentication Method
-
Name
-
IPsec Primary Gateway Name or Address
-
IPsec Secondary Gateway Name or Address
-
Shared Secret
-
Confirm Shared Secret
-
Local IKE ID
-
Remote IKE ID
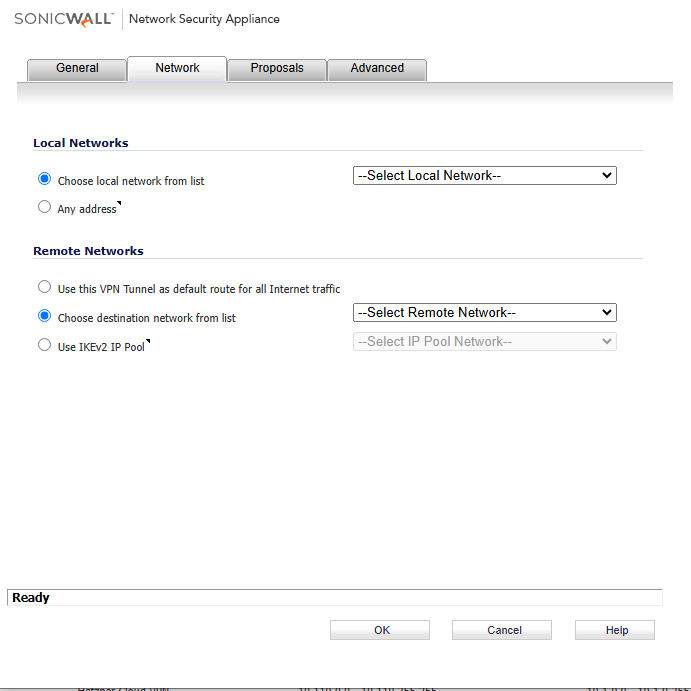
3.2 Network Values
-
Choose local network from list
-
Any address
-
Use the VPN Tunnel as default route for all Internet traffic
-
Choose destination network from list
-
Use IKEv2 IP Pool
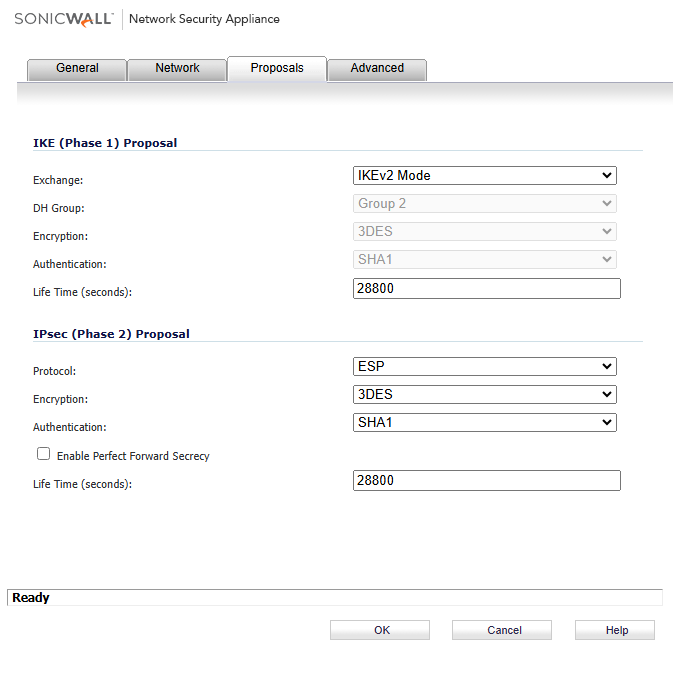
3.3 Proposals Values
-
IKE (Phase 1) Proposal
-
Exchange
-
DH Group
-
Encryption
-
Authentication
-
Life Time (seconds)
-
IPsec (Phase 2) Proposal
-
Protocol
-
Encryption
-
Authentication
-
Enable Perfect Forward Secrecy
-
Life Time (seconds)
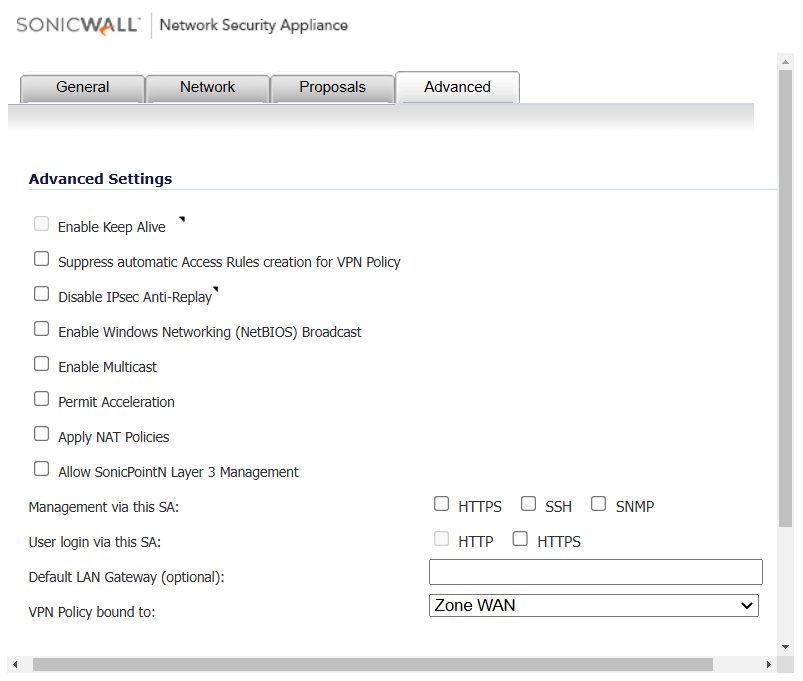
3.4 Advanced Values
-
Advanced Settings
-
Enable Keep Alive
-
Suppress automatic Access Rules creation vor VPN Policy
-
Disable IPsec Anty-Replay
-
Enable Windows Networking (NetBIOS) Broadcast
-
Enable Multicast
-
Permit Accelaration
-
Apply NAT Policies
-
Allow SonicPointN Layer 3 Management
-
Management via this SA
-
User login via this SA
-
Default LAN Gateway (Optional)
-
VPN Policy bound to
-
IKEv2 Settings
-
Do not send trigger packet during IKE SA negotiation
-
Accept Hash & URL Certificate Type
-
Send Hash & URL Certificate Type
4. Check the tunnel status
4.1 On Sonicwall webpage navigate to VPN/Settings and find the tunnel in VPN Policies section.
4.2 Test connectivity using ping or traceroute utilities.